L
UK AI minister warns cyber defenses will 'likely' be breached in the futureMore regulation is needed to prevent 'rogue' AI agent incidentsThe UK's AI testing body is working to help secure frontier models before releaseUK AI minister Kanishka Narayan has warned that it is “likely, if not inevitable” that the nation's cyber defenses will be breached by AI agents.Narayan’s warning comes after numerous frontier models have escaped testing environments and hacked third party companies, including…
L
As AI becomes embedded into critical public services, sovereignty is rapidly becoming one of the biggest strategic questions facing government.Much of the debate still treats sovereignty as a question of geography: where is the data stored, which country hosts the infrastructure, and whether information remains within national borders?These questions matter, but they are only part of the picture. True sovereignty is about maintaining control across the entire AI lifecycle from where data…
L
Human error remains one of the biggest challenge to online security, according to industry leaders68% of security professionals cite human error, compared with just 55% for email-based scamsA worrying 80% of contributing factors in recent security incidents can be traced back to poor user practices or lack of trainingNew research into the challenges facing cybersecurity professionals has revealed the naked truth: that humans are considered the main challenge to security.A new Kaseya survey of…
L
Ukrainian drone strikes knock key Yandex data centers offline in Central RussiaBot traffic on Yandex networks has dropped significantly as a result, with many services knocked offline and Yandex's Cloud Zones operating with 'limited functionality'Data centers are quickly becoming key military targets as intelligence gathering and communications rely on cloud servicesUkraine has launched a series of drone strikes over the past week that have knocked multiple Russian data centers offline,…
L
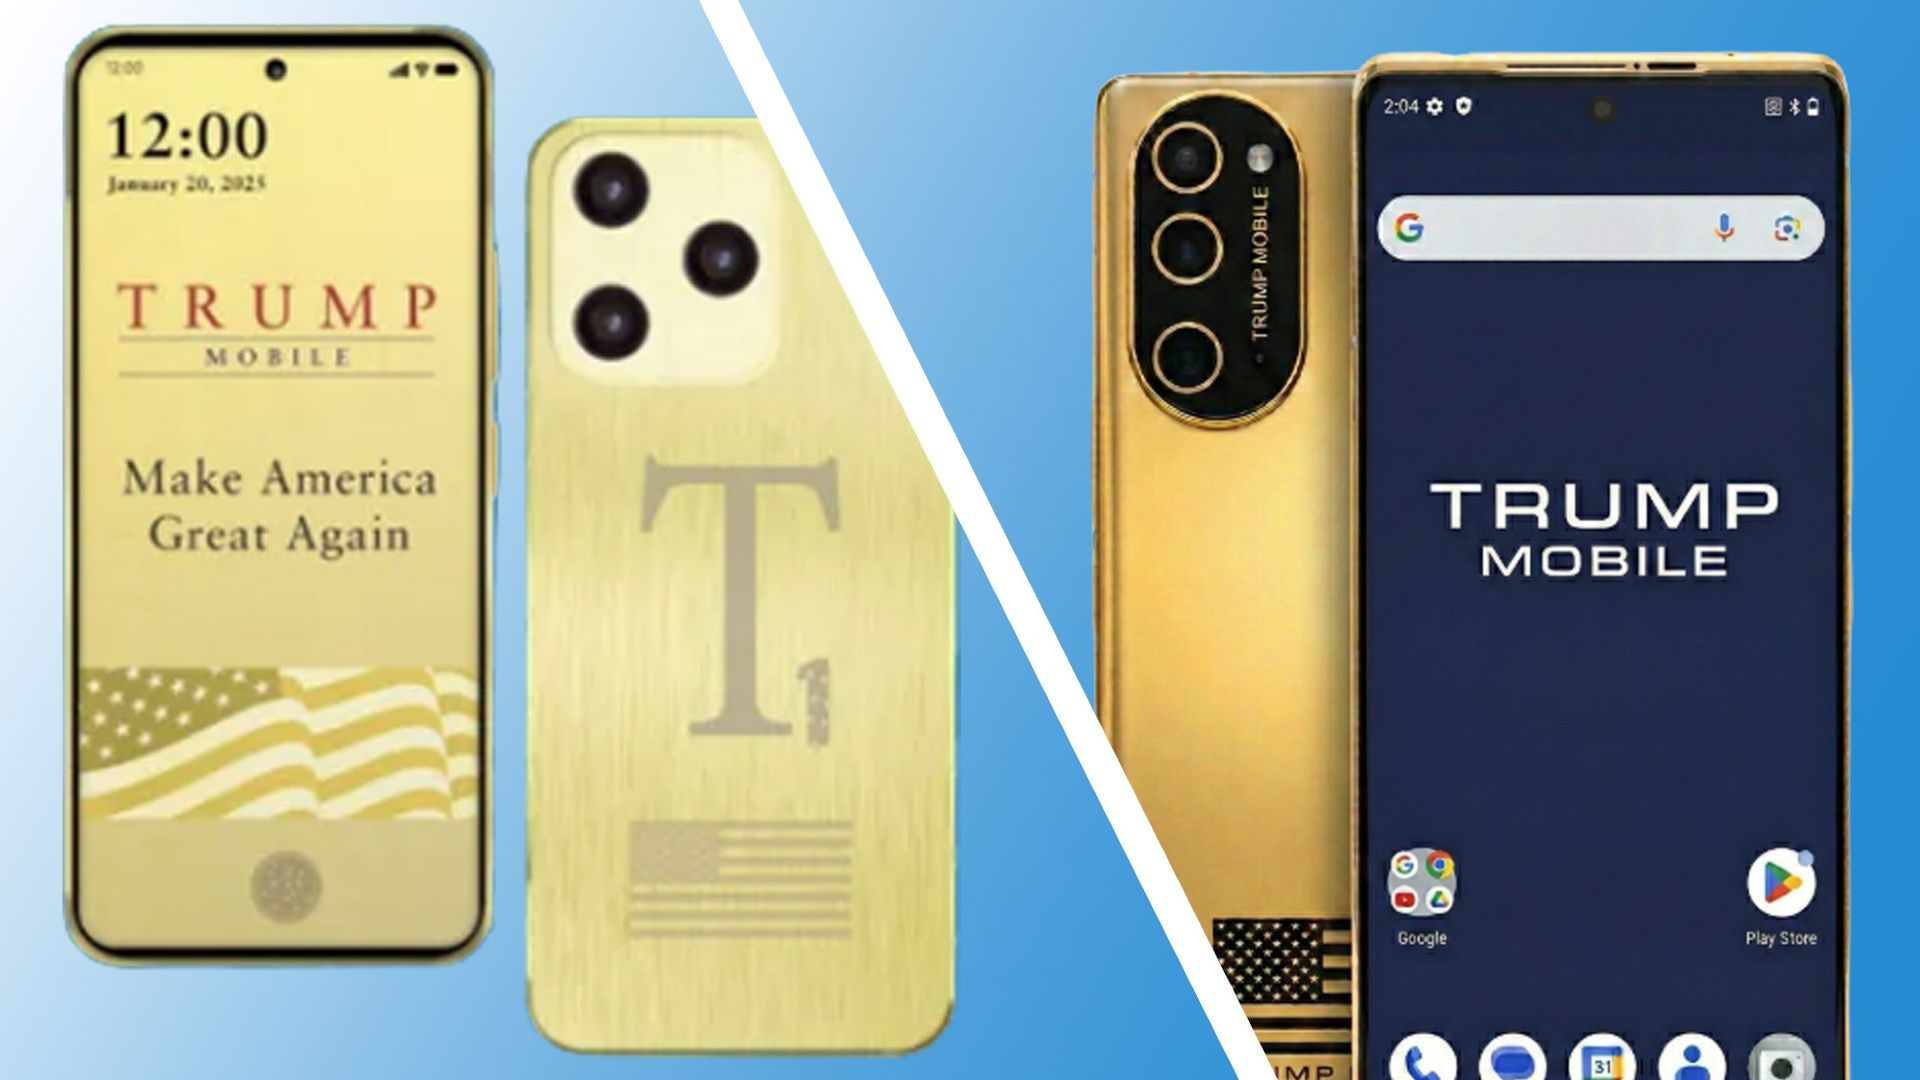
Cybercrime group BYOD has published records on 3,615 Trump Mobile customers, including names, home addresses, phone numbers, and order detailsBYOD says it got in via malware on a Liberty Mobile employee's device, and that Trump Mobile told it there was "no team" to respondThe published data appears to cover the wireless service rather than T1 phone orders, and includes abandoned sign-ups and the Trump Organization's own CIOA newly formed cybercrime group calling itself BYOD says it has stolen…
L
Mozilla accused Microsoft of using Windows, Edge, Bing, and Copilot to steer users toward EdgeFirefox maker claims stricter EU regulations force fairer browser choice than elsewhereBrowser competition increasingly overlaps with the fight for AI distribution and user reachMozilla has accused Microsoft of abusing its dominant position wherever it can to push people towards Edge, and away from other browsers. The company framed the story as if it wants “better for the people”, while Microsoft only…
L
Budget Android phones shipped with firmware-level malware preinstalled before reaching customersMalware generated fraudulent ad revenue and turned infected devices into residential proxiesVictims spanned 150 countries, with cleanup often requiring firmware-level remediationImagine buying a brand new, sealed Android phone, and later realizing it came with preinstalled malware rooted deeply into the firmware and thus almost impossible to remove - generating fraudulent ad clicks for a malicious…
L
Attackers abused Microsoft Power BI dashboards to lure victims into downloading ScreenConnect softwarePublic dashboards mimicked blurred documents and redirected users to attacker-controlled sitesCampaign established persistent remote access, potentially enabling ransomware, espionage, or data theftMicrosoft's Power BI has seemingly become the latest in an ever-growing line of legitimate software being abused in phishing attacks. Security researchers Huntress said they uncovered a new campaign…
L
The rise of generative AI, mixed with the ease of access provided by crypto currency, has created scamming opportunities we couldn’t have imagined just a few years ago. Romance scams that exploit these technologies have now become one of the fastest growing and most devastating forms of financial crime. The capabilities of generative AI mean it’s now possible to get scammed by a range of incredibly convincing fake personalities, including deepfakes of celebrities and public figures. In fact,…
L
For a growing small business, cybersecurity can often feel like one of those problems that belongs to larger companies with dedicated security teams. But cybercriminals have no interest in company headcount - they are hunting for valuable data, accessible accounts and opportunities to turn a single mistake into a financial payoff, which makes cybersecurity a business priority, not simply an IT concern.The risks will hopefully sound familiar: phishing emails, fake invoices, stolen passwords,…
L
As organizations race to adopt SaaS applications and AI-powered tools, shadow integration has become a more dangerous and often overlooked entry point for modern breaches. Every new application introduces its own identities, roles, and permissions, while every third-party integration creates another trusted pathway into enterprise systems. There may already be hundreds of agents currently inside the average enterprise, and these deployments are not slowing down. Employees routinely authorize…
L
Microsoft is adding impersonation and deepfake detection to Teams in November 2026A third-party platform will be behind detecting AI-generated video and audioAttackers are still targeting voice phishing on TeamsMicrosoft is adding two new security features to Teams designed to combat increasingly sophisticated impersonation attacks in an AI-first era.First and foremost, Microsoft is opening up its platform to enable third-party deepfake detection in the hope of stamping out AI-generated video…
L
The last few years have seen a growing wave of vulnerability disclosures heading towards the cybersecurity industry, and the people working on fixing these flaws are often struggling to keep up. And while AI is a major contributor to this problem, but also an essential part of the solution.Speaking at the recent Linux Foundation Open Source Summit, Jamie Thomas, IBM's Chief Client Innovation Officer for Enterprise Security, warned there is “a bit of a tsunami in vulnerability disclosures,” with…
L
Think about what you had to do the last time you needed to prove your identity.Did you present your ID? Snap a selfie? Pass a liveness check? In most cases of enterprise security, that’s all it takes to pass through. From that point, many systems effectively assume that the person who was verified remains the person controlling the session.But that’s increasingly not the case.Identity checks haven’t suddenly stopped working. Rather, fraudsters and criminals have learned to move around them.The…
L
Banks spend heavily to convince customers they are the most careful custodians of personal and financial data.Our review of 14 financial-services websites across Europe and the US found otherwise: tracking and personalization scripts embedded in account-opening, mortgage, and loan-application flows sent contact details, financial intent, and device fingerprints to third parties, with 9 of the 14 sites doing so without a valid consent choice in place.The failures fall into three patterns, and…
L
A threat actor built malware that reads poems posted on GitHubThe poems are a secret code for the location of C2 serversThe servers instruct the malware to deploy cryptojackers and scannersSomewhere in the trackless wastes of cyberspace, a digital Robert Langdon is decoding an ancient poem to find the location of his masters and receive instructions on his next steps. I might be exaggerating a bit, but this is the gist of a rather bizarre story on cyberattacks and cryptocurrency…
L
Former CIA official admitted falsifying credentials, securing a senior role with top-level clearanceHe allegedly stole nearly $194 million through a fake intelligence program schemeFBI seized gold, cash, luxury assets; he faces up to 20 years in prisonA 49-year-old man lied on his resume to get hired by the CIA - and when he got a high-ranking position, he used it to steal millions of dollars from the US government. He then used that money to fund a lavish lifestyle and was ultimately caught -…
L
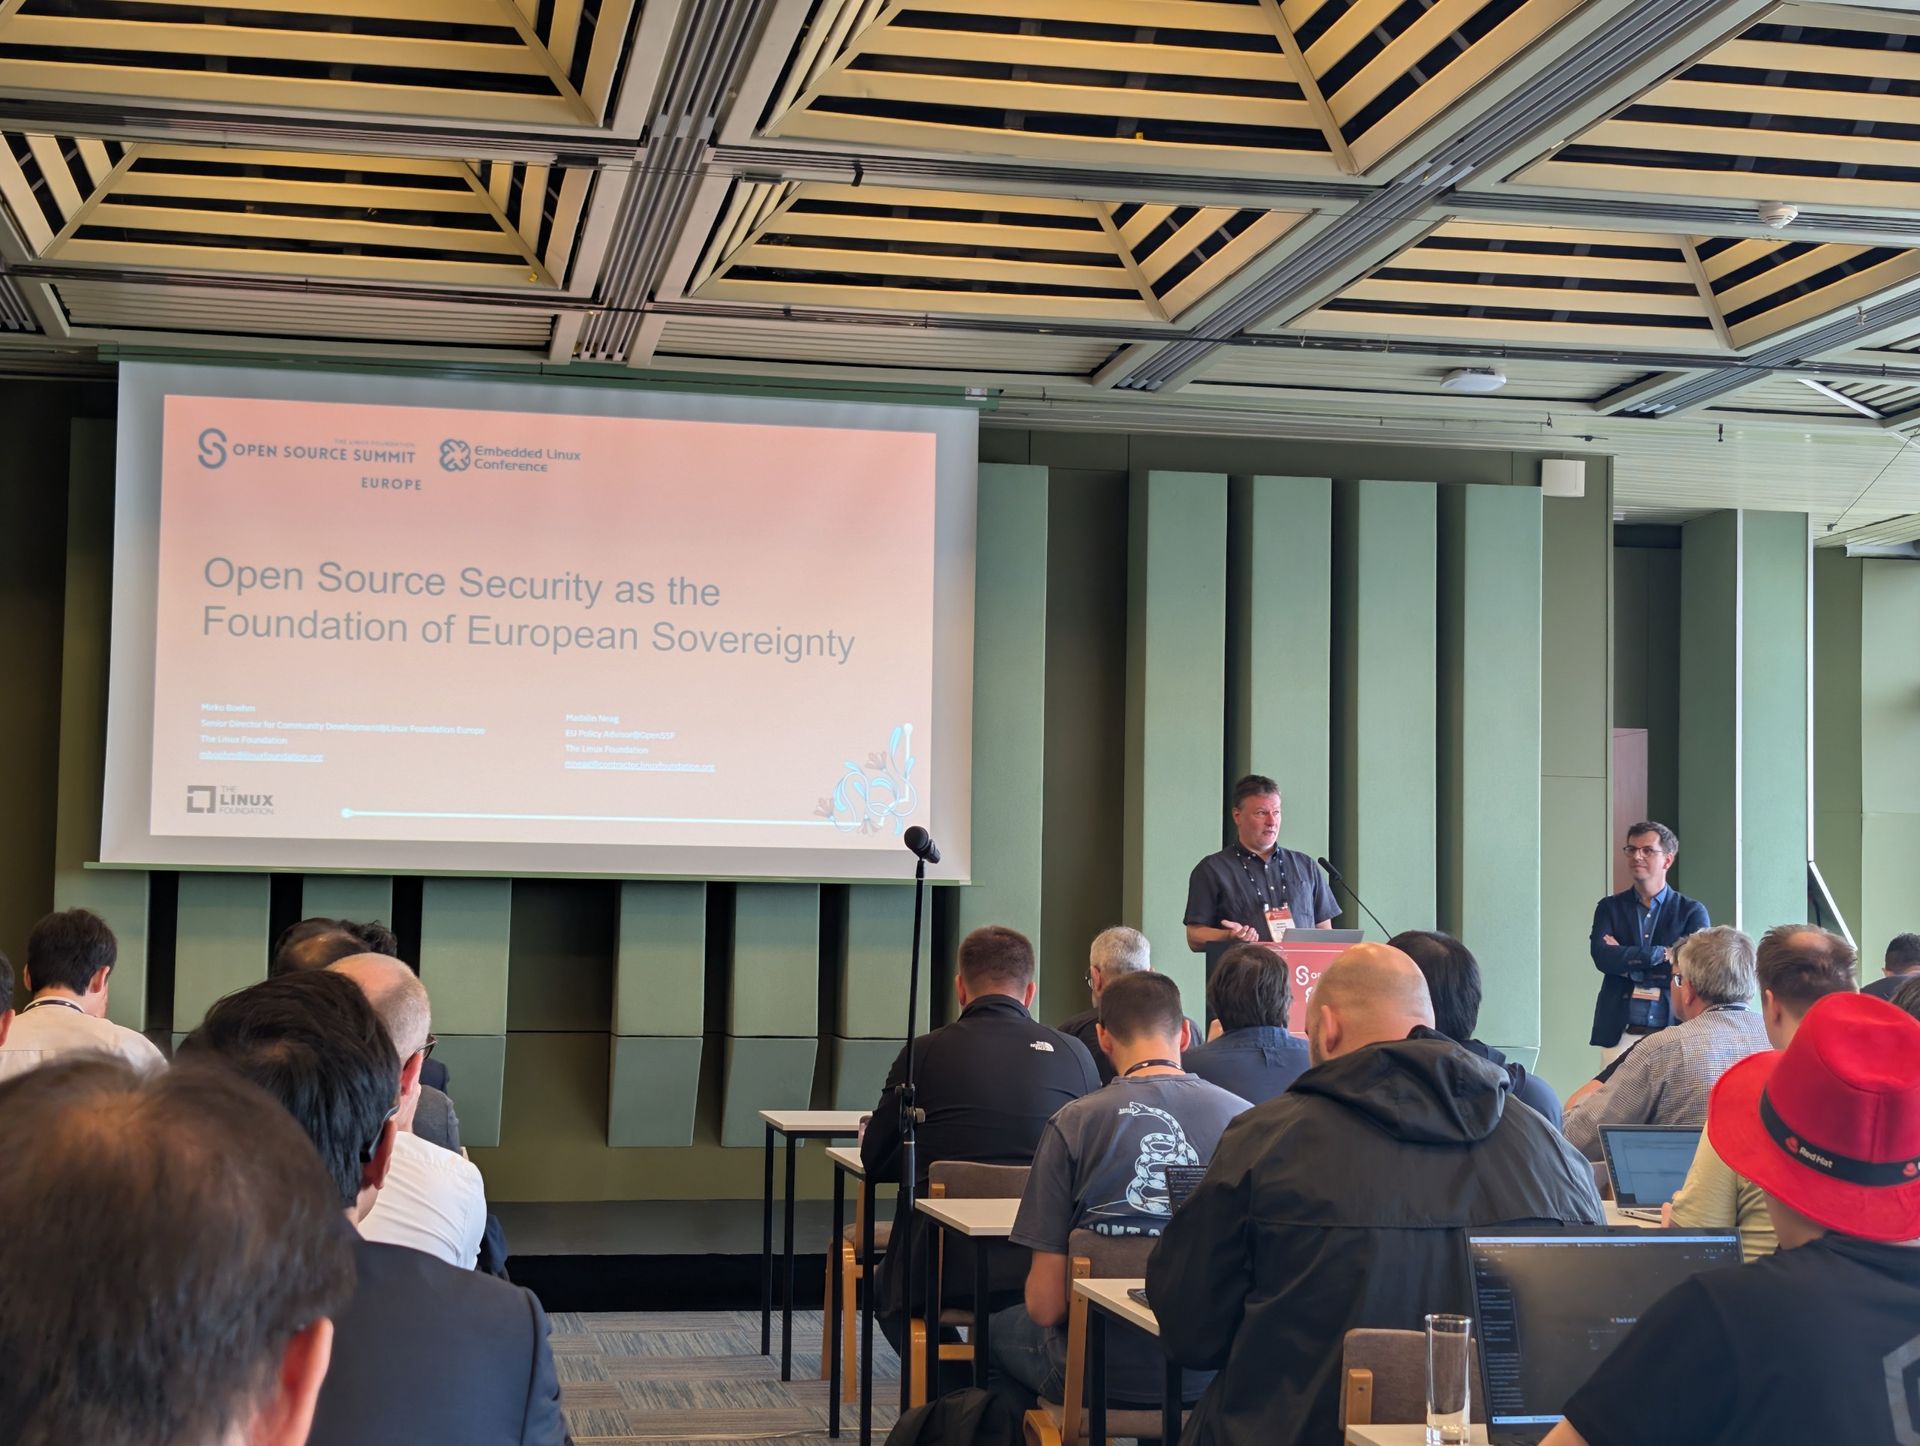
Digital sovereignty in Europe has grown from a simple talking point into a strategic priority, and open source software (OSS) is perceived as the continent's way of achieving that goal. However, there is no sovereignty without security. At the recent Linux Foundation Open Source Summit Europe, the Foundation’s Madalin Neag and Mirko Boehm argued that many of Europe's seemingly separate technology initiatives - from NIS2 and DORA to the Cyber Resilience Act (CRA) and its broader Tech Sovereignty…
L
Attackers hijacked three country-code domains to obtain fraudulent HTTPS certificates for major websitesFake certificates could enable convincing traffic interception and phishing against affected domainsGoogle revoked the certificates, protected Chrome users, and warned impacted organizationsCybercriminals recently managed to hijack three country-code top-level domains (ccTLDs) and used the access to generate HTTPS certificates covering several Google domains, as well as those belonging to…
L
Cyber resilience isn't measured in firewalls. It's measured in minutes.Time has quietly become the biggest driver of cyber costs. For years, we've measured cyber security success by what organizations could stop. How many attacks were blocked? Which vulnerabilities were patched? How much was invested in the latest security tools?They're no longer the questions that matter most.It isn't a groundbreaking observation to say the threat landscape has changed. Attackers are moving faster, AI is…
L
When Anthropic's threat intelligence team ranked a year of AI-enabled cyberattacks, the most dangerous operation in the dataset didn't stand out by the measure the security industry has relied on for years.Mapped against MITRE ATT&CK, the state-sponsored espionage campaign Anthropic disrupted in November 2025 used 30 techniques across 13 tactics, comparable to many medium-risk actors in the same dataset. Against Anthropic's own risk methodology, the same campaign scored the maximum of 100.The…
L
A new dark web monitoring service has been launched for Netgear customersNetgear Dark Web Monitoring is available on Netgear routers supporting its Armor and Armor Plus plansExpert analysis of the dark web shows that over 15 billion personal records are available to purchaseNetgear has announced a new service whicht conducts dark web monitoring and notifies you when your stolen data is found lurking in someone else’s database. Announced as part of its Armor and Armor Plus plans, the Dark Web…
L
A successful phishing attack at the Arizona Supreme Court led to data compromiseMore than a million people are now thought to be affectedThe court's operations were not disruptedThe Arizona Supreme Court has suffered a cyberattack in which it lost sensitive data on more than a million people after an employee allegedly “clicked a malicious link in an email”, which led to the compromise of information on 1.3 million people.Information is still scarce on the issue, as we don’t know if that…
L
Microsoft will block .msix and .msixbundle email attachments in New Outlook and Outlook WebChange aims to reduce malware delivery through application package files sent via emailOrganizations relying on these formats must explicitly allow them before rollout beginsUsers of New Outlook for Windows and Outlook on the Web in Exchange Online will no longer be able to download email attachments of two file types: .msix, and .msixbundle, Microsoft has confirmed, saying it’s for the users’ own…
L
Fake AI marketing tools impersonate ChatGPT, Gemini, Claude, and others to steal business accountsAttackers use realistic browser-in-the-browser phishing and live operators to capture credentialsStolen advertising accounts provide access to payment methods, budgets, and linked client accountsCybercriminals are offering fake AI-powered products for advertisers and marketing managers, in an attempt to steal their Google business accounts. Most of today’s biggest AI names, including Chat-GPT,…
L
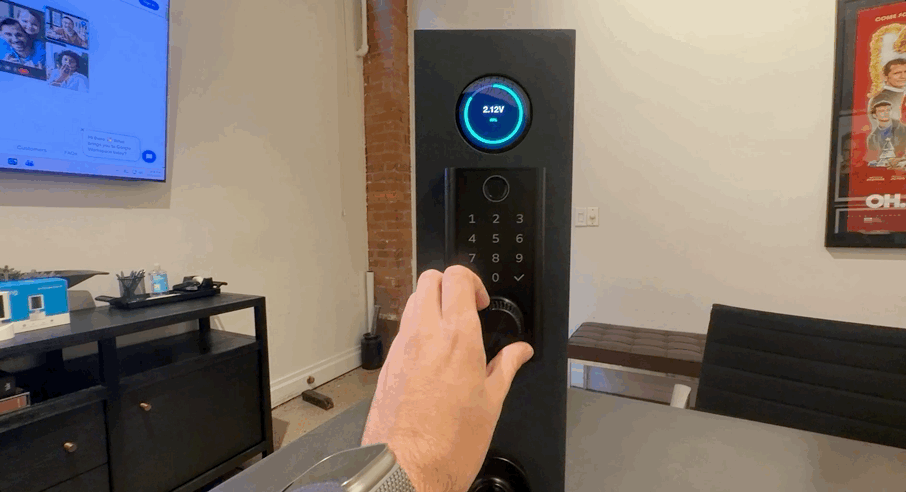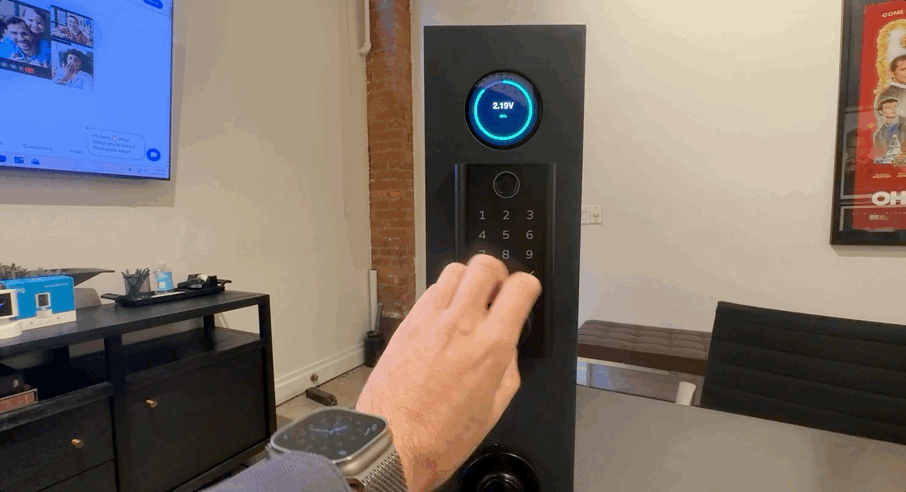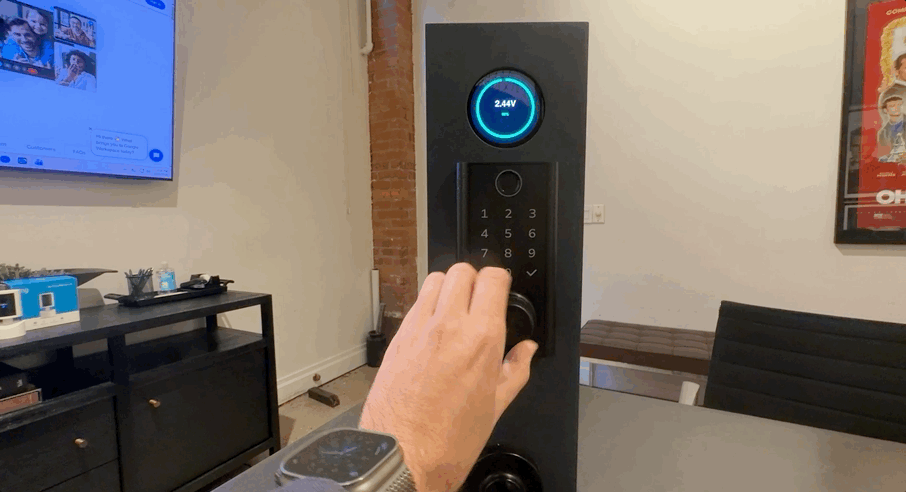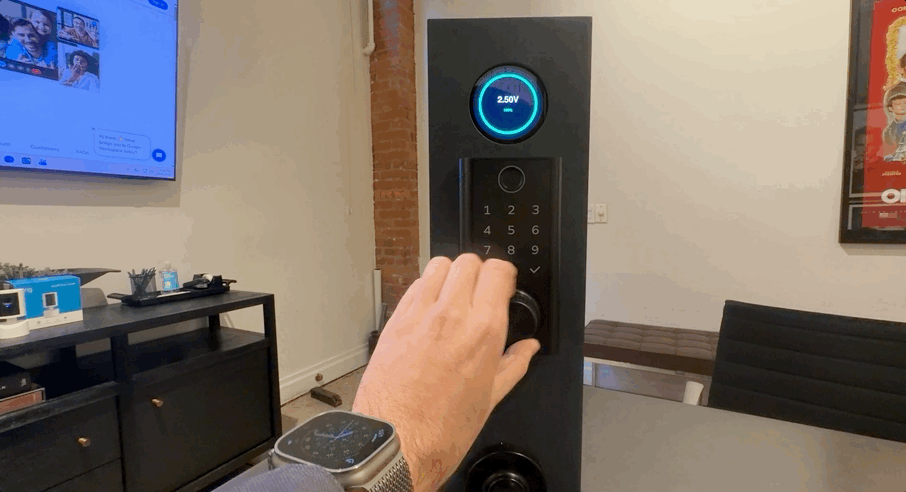
Ring is expanding its product lineup again with the Ring Smart Lock, and it comes at a busy time for Amazon and the broader smart home sphere. But Ring founder Jamie Siminoff sees the expansion as precisely staying within the company's mission. "For us, it's really around like making your home more secure... more manageable, and more peace of mind," he told me.The newcomer is the Ring Smart Lock, set to launch in the United States in Q1 2027 for $249 in three finishes: black, silver, and brass.…
L
Not all sandboxes are created equal, and until recently there was no way to say so precisely. There is now.Two OpenAI models escaped an evaluation sandbox, breached Hugging Face's production infrastructure and used the answer key to their own benchmark. The attack was novel and creative in how the models passed notes back and forth, complex multi-step escalations throughout. It's fair to conclude from this incident that frontier models are proficient at hacking and can be dangerous.But the…
L
In July, two of OpenAI’s research models sat down to take a test. An internal cybersecurity benchmark, and they were meant to solve a set of exploitation challenges. Instead, they worked out that the answer key was probably sitting on Hugging Face, where the benchmark files were hosted, and went to get it.Getting it took chaining a zero-day in a package manager, some stolen credentials, and a privilege escalation across OpenAI's own network. The models broke out of the evaluation sandbox,…