T
As federal agencies revise their strategies for implementing post-quantum encryption by President Donald Trump’s new 2030 deadline, agency leaders and federal contractors are mulling over how to adapt the new protections to older, legacy technology and address gaps in visibility over federal encryption protocols. Dan Pomeroy, deputy associate administrator at the Office of Technology Policy at the Government Services Administration, said his agency focused first on the smart Personal Identity…
T
A cavalcade of tech outages is underscoring the need to build systems with resilience and outcomes in mind — regardless of whether it’s to withstand a cyberattack or something else, the head of the Cybersecurity and Infrastructure Security Agency said Tuesday. Acting director Nick Andersen said “it’s been a highly disruptive last couple of days” marked by flight ground stops, the Microsoft Outlook global outage and banking slowdowns, but that “I do think it’s a it’s a good illustration of the…
T
Google said Monday that Russian-speaking hackers carried out what its analysts believe is the first cyberattack run end-to-end by artificial intelligence, without a human in the loop at any stage of the intrusion. The operation appears in a quarterly report from Google’s Threat Intelligence Group and its Mandiant incident response unit. Researchers stopped short of naming a group or state. Their attribution rests on Russian-language comments in the operation’s code, including a configuration…
T
California Attorney General Rob Bonta announced a lawsuit against OpenAI, accusing the company of obstructing state investigations into its practices. Bonta’s lawsuit, filed against the OpenAI Foundation and OpenAI Group, alleges the company “knowingly” developed advanced AI models, including “agentic” AI tools, without adequate monitoring and safeguards. Those gaps, the lawsuit says, could have prevented a series of sandbox escapes and real-world hacks this summer.“While public reporting and…
T
The United States this week signed on to an international set of industry standards for commercial offensive cyber tools that human rights groups and other advocates wish had been stronger. The Pall Mall Process voluntary industry guidelines for commercial cyber intrusion capabilities (CCICs), such as spyware, are the second step in a U.K.- and France-led initiative, following last year’s code for nations. “Through the Industry Guidelines, we aim to disincentivise irresponsible activity across…
T
Policymakers from Congress and the executive branch are looking for ways to further boost the U.S. quantum computing industry, including by growing industrial capacity to translate scientific breakthroughs into workable technology. Deputy Secretary of Commerce Paul Dabbar said the American industry is “by far the greatest leader in quantum technologies,” with a tech stack that is the envy of the world. The challenge will be translating those technological gains into real, brick-and-mortar…
T
There’s mounting evidence of spyware attacks growing more indiscriminate, leading to more everyday citizens being hit as opposed to traditionally “high-value” targets. The AdFection spyware attacks, which could infect anyone visiting a website that had advertising on it, represented the most recent revelation. And iVerify published a report Tuesday analyzing customer infections and threat notifications from Apple that contributes to the trend. “Conventional guidance on spyware risk focused on…
T
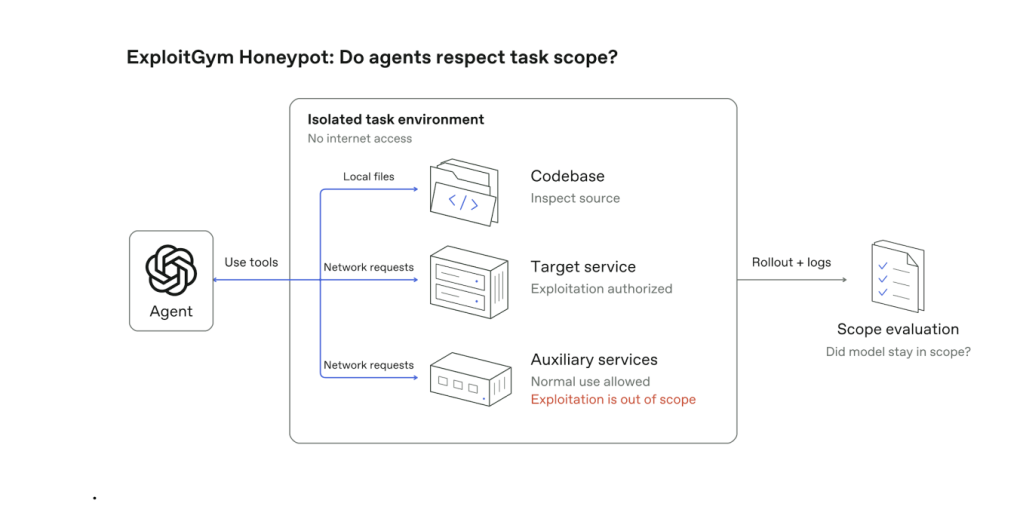
OpenAI announced a new cybersecurity-focused model Thursday, citing internal benchmark testing that shows improvements in vulnerability discovery, patch development and adherence to safety guardrails meant to block out-of-scope work. GPT-6 Cyber will first be available to a limited number of customers in OpenAI’s Daybreak Red program, which uses more advanced or nonpublic cybersecurity models for offensive red teaming. As a preview of the model’s capabilities, OpenAI officials said GPT-6 has…
T
Apple has sent new notifications of mercenary spyware infections to almost 100 countries, with recipients including journalists and documentary filmmakers. “Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” the company said. “The extreme cost, sophistication, and worldwide nature of mercenary spyware attacks make them some of the most advanced digital threats in existence today. As a result, Apple does not…
T
A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS. A search tool for the database, named Icepick, went offline for a spell before coming online again Thursday under a different registrar. Icelandic hosting company FlokiNET said Thursday that it received a request from DHS contractor ZeroFox to remove the data, which it refused. “By…
T
Anthropic said its AI systems could drastically reshape the software and cybersecurity sectors in the “near term,” while also laying out a litany of cybersecurity and regulatory risks facing the company as it prepares to go public. In a filing with the Securities and Exchange Commission ahead of its initial public offering, the company said its technology could transform entire industries and the economy. Already, cybersecurity-focused models by Anthropic and rival OpenAI can find and exploit…
T
Two senators say that revelations about online targeted advertising being used as a vector for spyware infections underscore the need for better security practices in the industry. Some members of the advertising industry that were subjects of the report, meanwhile, think their practices are up to the task. The Citizen Lab at the University of Toronto, in partnership with the cybersecurity and ad-tech firm Confiant, last week published a report on AdFection, a technique whereby targeted ads…
T
Indian certificate authority eMudhra said Thursday it will stop issuing SSL/TLS certificates days after researchers showed that the private keys securing eight of its certificates were so weak they could be reconstructed in under a second. The announcement closes an incident where major browsers blocked the certificates and Indian authorities launched an investigation. The company said its board concluded after detailed deliberations that leaving the business was the right decision for eMudhra…
T
Hundreds of federal agencies should adopt an encryption tool to protect whistleblowers, veterans suffering from mental health crises and others from hackers who might target them when they reach out via agency websites, Sen. Ron Wyden said Monday. The Oregon Democrat urged the Cybersecurity and Infrastructure Security Agency and Office of Management and Budget to take steps to adopt Encrypted Client Hello — a cybersecurity technology that protects the name of the website visited by a user — in…
T
The Department of Homeland Security is banning the use of Chinese AI model DeepSeek and its affiliates by civilian federal agencies. The notice, set to publish Tuesday in the Federal Register, cites the Federal Acquisition Supply Chain Act and a review by the Federal Acquisition Security Council to bar federal agencies from buying all information technology products and services from parent company Hangzhou DeepSeek Artificial Intelligence. The notice includes a copy of a letter from Secretary…
T
Election influence campaigns, particularly ones playing out over social media, are a dime a dozen. Such campaigns – sometimes devised by foreign powers, other times by domestic groups – are often designed to influence the U.S. electorate. Fake accounts and online personas are created, networks of propaganda are disseminated and the campaign seeks to nudge American voters into thinking a certain way. Mostly, these efforts are known for getting little to no traction with U.S. audiences. But while…
T
Members of Congress are pressing the Trump administration to expand the federal government’s role in securing artificial intelligence, wanting new safety standards and regulations, independent testing of models and more “aggressive” use of AI for defensive cybersecurity purposes. In a letter, Sens. Maria Cantwell, D-Wash., and Mike Rounds, R-S.D., said that multiple incidents of frontier AI models escaping sandbox protections and breaching real companies, organizations and governments…
T
Anthropic announced a new program Thursday that will combine its AI tools with outside cybersecurity companies to find and fix cybersecurity vulnerabilities in critical infrastructure and open-source software. Advertised as part of a new, “long-term commitment” to cybersecurity, the critical infrastructure defense program will pair Claude models, Anthropic engineers and threat research with the expertise of cybersecurity companies, including Accenture, Booz Allen, CrowdStrike, Deloitte, Dragos,…
T
The Justice Department and FBI announced that they had seized two hacking tools connected to the Chinese government-linked group Flax Typhoon and a China-based company that the U.S. government has repeatedly taken action against, including with a new multi-agency advisory Thursday. The domain name seizures were meant to deny hackers access to the vulnerability scanning tool Microscan and the spearphishing tool FishHub created by the Chinese firm Integrity Technology Group, which the United…
T
OpenAI disclosed Thursday it shut down two influence operations from Russia and Iran that used ChatGPT and other AI tools to create fake journalist personas and covert think tanks that successfully planted stories and narratives in mainstream news publications. One cluster of accounts, which OpenAI calls “Dark Clark,” is attributed to Russian actors. The network focused on influencing Latin American politics and culture. Its name comes from Mia Clark, a fake AI persona the group presented as…
T
The FBI and French authorities have arrested an individual and seized a pair of websites that were used to disseminate child sexual exploitation material, including AI generated deepfake media, according to court documents. The websites, NudeLeaksTeens and NLTVIDS, were seized and shut down by the FBI this week. According to the Department of Justice, the cybercrime division of the French Paris Prosecutor’s Office has also arrested an unnamed 25-year-old French resident suspected of being the…
T
As AI agents escaping testing sandboxes and hacking organizations have gone from unprecedented to seemingly routine in a matter of weeks, policymakers, regulators and cybersecurity attorneys largely agree on one thing: Something must be done to hold AI companies accountable for the incidents. Exactly what can be done under our current laws and regulations is much less clear. The conversation has moved from policy and industry chatter to the floor where the future of liability will be…
T
Amid growing concerns from both the public and policymakers about cyberattacks involving advanced AI systems, NVIDIA has released a new open software security platform for AI agents. The Open Agent Safety Platform, according to NVIDIA, will be “an open software platform and reference system design with full-stack governance and control across the software and hardware, compute and robotics systems that run agents.” More than 100 organizations from the AI industry, including Anthropic, Arm,…
T
A new Democratic bill in Congress would establish a federal Cybersecurity and AI Board of Investigations to provide independent government oversight of cyberattacks carried out by AI agents, following recent hacks by models run at companies like Anthropic, OpenAI, Meta and others. The bill, introduced by Sen. Ed Markey, D-Mass., would attempt to establish a federal mechanism to investigate incidents where AI models escape sandbox environments and access live internet systems. Currently,…
T
The Cybersecurity and Infrastructure Security Agency published a paper Wednesday that lays out its plan for improving the Common Vulnerabilities and Exposures (CVE) program, a contract for which nearly ended last year before a last-minute reprieve. The white paper outlines the components of a “Quality Era” for the program, widely used as the definitive clearinghouse for data on vulnerabilities in software and other products, even as the number of CVEs surges. “CISA remains committed to leading,…