M
In this article A new cyber stack, built to fight AI with AI Delivering agentic security at Microsoft IgniteSecure your foundations Defend with agents Secure agentic insiders Changing how security work gets done Explore what's new A year ago, finding a serious, exploitable vulnerability was slow and expensive work done by elite security researchers. That’s no longer true. Over the past 12 months, frontier AI models have become remarkably good at discovering and exploiting software…
M
Endpoint administrators need to keep elevated access accountable at scale. Security teams also need a clearer view of expert-led protection and a simpler way to deploy SQL Server protection in Azure Government. As AI agents gain access to business data and tools, organizations need ways to limit their authority and adapt protection as risk changes. This month’s Microsoft Intune and Microsoft Defender updates introduce capabilities across these areas, alongside new Secure AI capabilities for…
M
October is Cybersecurity Awareness Month, and it’s a good time to think about how much the world has changed for chief information security officers (CISOs) in the last 12 months. A year ago, we thought we were already in the thick of AI and starting to understand it. Since then, agents have spread across the enterprise faster than most organizations anticipated. According to our Work Trend Index Annual Report, the number of active agents in the Microsoft 365 ecosystem grew 15-fold year over…
M
In this article What’s happeningWhat is ARTEX?Mitigation and protection guidanceReferencesLearn more As early as September 2026, Storm-0940, a China-state aligned actor, used the agentic AI penetration testing framework ARTEX to automate attacks targeting hundreds of organizations globally across a broad range of industries. Several of these Storm-0940 ARTEX-driven attacks have resulted in the actor obtaining privileged access to an organization’s cloud infrastructure – including multiple…
M
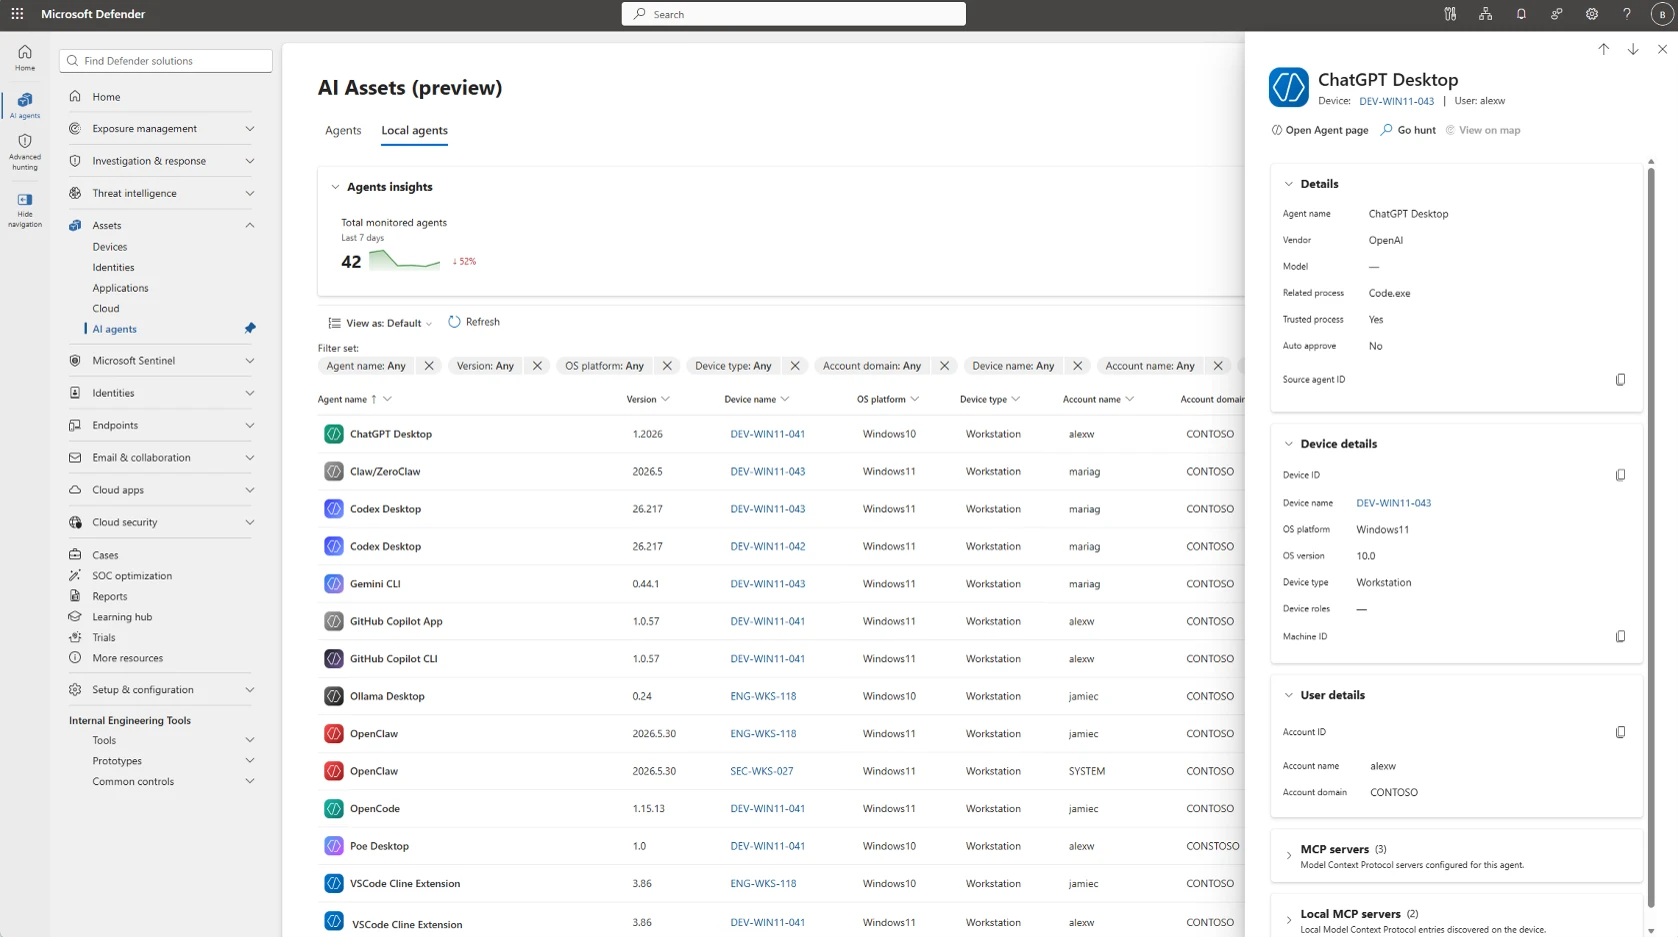
AI agents are now running on employee devices, cloud platforms, and across developer workflows. Security teams need to see those agents, govern what they can reach, and contain them when something goes wrong. This month’s updates help you discover and control local AI agents, extend Zero Trust to agent traffic, and strengthen the security operations center (SOC) foundations that AI-era operations depend on. Here’s what’s new: Extend protection and support investigations with Microsoft Defender…
M
As organizations incorporate AI agents into more processes across business and operations, security teams can benefit from greater visibility and new purpose-built tools that help manage, secure, and govern AI. This month’s updates provide new capabilities to help organizations gain insights into agent activity, expand security coverage across supported environments, and enhance security management across their environments. Here’s what’s new: Extend expert-led protection with new capabilities…
M
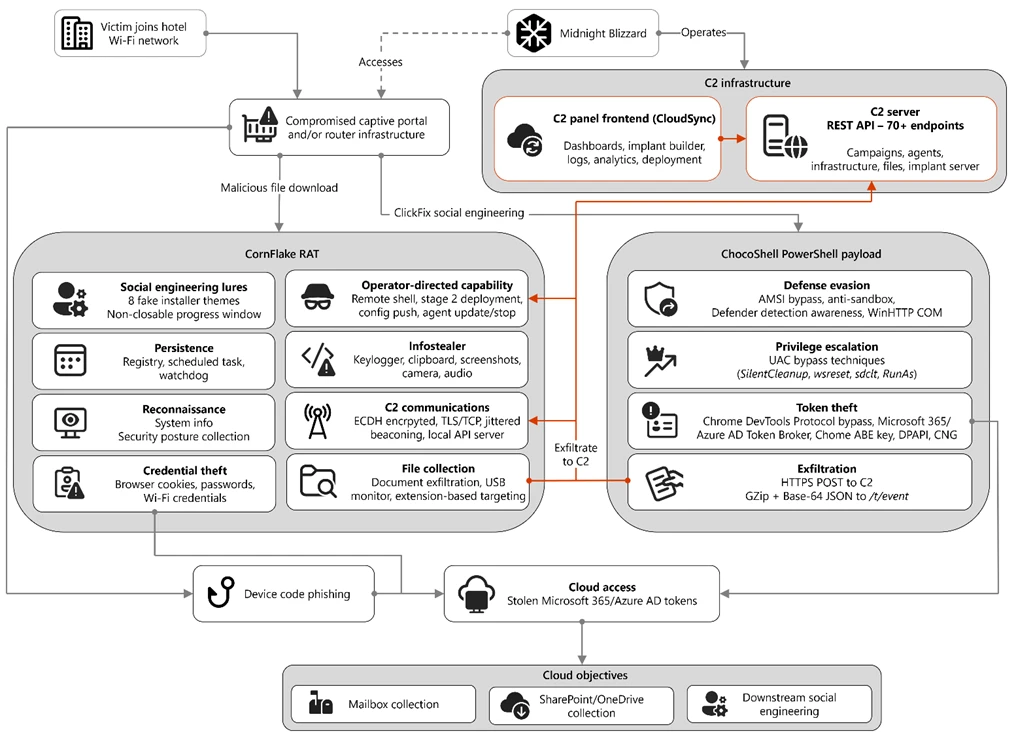
In this article The CaptiveCrunch campaignStorm-2945 and Midnight BlizzardCaptiveCrunch tradecraft and toolingHow to protect against CaptiveCrunch activityMicrosoft Defender detections and hunting guidanceIndicators of compromise October 5, 2026 update: On September 29, 2026, Microsoft Threat Intelligence observed Storm-2945, a sub-cluster of Midnight Blizzard, resuming their CaptiveCrunch campaign, using manipulated network traffic and captive portals in the hospitality sector to gain access…
M
Every organization needs security that protects end to end with the speed and scale of AI. Microsoft’s vision is simple: security should be ambient and autonomous, just like the AI it protects. As organizations scale AI and expand across environments, security teams need protection that covers every surface. This month’s updates help security and IT teams secure their AI environments, use AI to defend at speed and scale, and strengthen the foundations that AI-powered operations depend on.…
M
As identity attacks grow more sophisticated in the AI era, organizations need stronger authentication methods that protect users from phishing, credential theft, and social engineering. To address these evolving threats, Microsoft Entra ID is updating its authentication experience by making passkeys the default phishing-resistant authentication method, helping customers reduce reliance on phishable methods such as SMS and voice. Beginning September 1, 2026, Microsoft will begin rolling out…
M
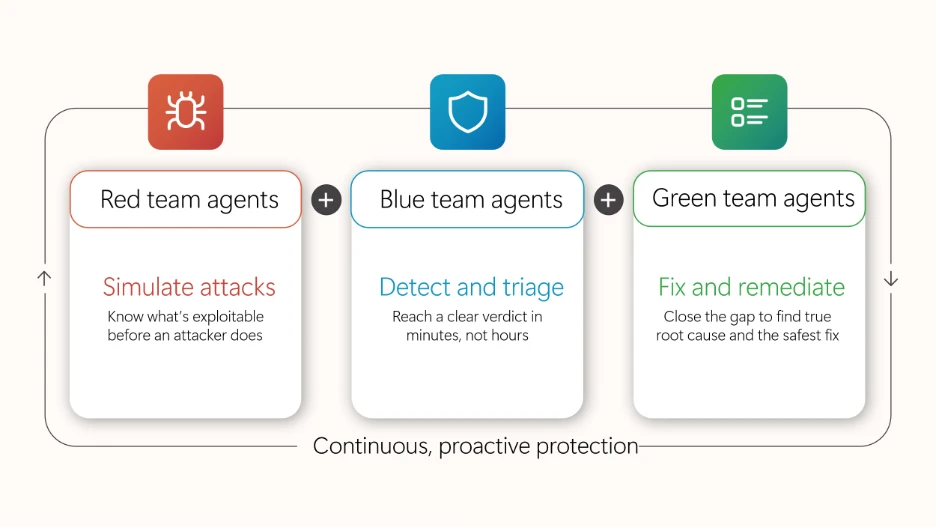
AI models have reached a threshold where they exhibit expert-level capabilities in vulnerability discovery, exploit chaining, and proof-of-concept generation. As AI-powered vulnerability discovery matures, every organization that builds or runs software at scale needs continuous proactive evaluation to ensure security controls are correctly implemented, layered effectively, and working as intended in production. At Microsoft we encompass these security requirements, along with threat knowledge…