L
Hackers and fraudsters are already gearing up to steal data and financial information in the run up to the US midterm electionsAI generated imagery and deepfakes are part of highly convincing scamsPhishing campaigns designed to prey on voter registration are also likely to pop upAs the US midterms rapidly approach, the FBI is once again warning Americans about the flood of election-related scam campaigns coming their way.Thousands of websites have already been spotted getting ready to spool up…
L
Cyberattack on BAE Systems disrupted the US Bankruptcy Noticing Center and halted bankruptcy notice distributionMultiple judiciary-related services and websites were temporarily taken offline during the incidentAuthorities and BAE are investigating the attack, with no details yet on data exposure or attributionBAE Systems recently suffered a cyberattack which disrupted the US Bankruptcy Noticing Center (BNC), a service that sends official notes and orders from US federal bankruptcy courts.The…
L
World ID for Zoom will put a Human Badge on your video feed to prove you're... humanSetting this up requires a physical iris scan and a verification selfieVerifying human authenticity is easier than identifying deepfakesSam Altman's biometric identity verification company, World, has launched a series of tools designed to help businesses distinguish real people from AI deepfakes as one of his other companies – OpenAI – becomes increasingly capable of mimicking humans.One of the main…
L
Burger King Japan discloses breach affecting 11.18 million customer records from its mobile app platformExposed data included personal details and order histories, though payment information was not compromisedCompany reported no confirmed misuse and notified regulators while investigating the intrusionThe Japanese subsidiary of Burger King has confirmed suffering a data breach and apologized for losing sensitive data on millions of customers. In a breach notification letter, Burger King Japan…
L
There’s never been so much change happening across an IT estate. And it’s constant. On a day-to-day basis, IT teams might be creating and monitoring user permissions, deploying any scheduled operating system (OS) updates or integrating new third-party software tools. This is not to mention all the change carried out by external providers, outsourced teams and employees.Change itself is not a problem. Indeed, it’s essential for ongoing security, resilience and modernization. Change that isn’t…
L
AI coding assistants are no longer experimental. In organizations that have adopted them, AI is responsible for roughly half of committed code. The question is, therefore, no longer whether developers will use AI, but whether security programs can govern what those systems produce. AI-generated code is remarkably good at producing syntactically correct code, with a 99.9% pass rate. In contrast, security performance tells a very different story.As it stands, the average security pass rate is…
L
Fake WatchGuard VPN website steals administrator credentials while delivering legitimate softwareAttackers collected VPN server addresses, usernames, and passwordsThe fraudulent website rejected initial submissions to collect credentials a second timeA fraudulent WatchGuard download website stole VPN login details while supplying the authentic installation package, experts have claimed.Security investigators at Huntress traced the activity to a lookalike domain that collected connection details…
L
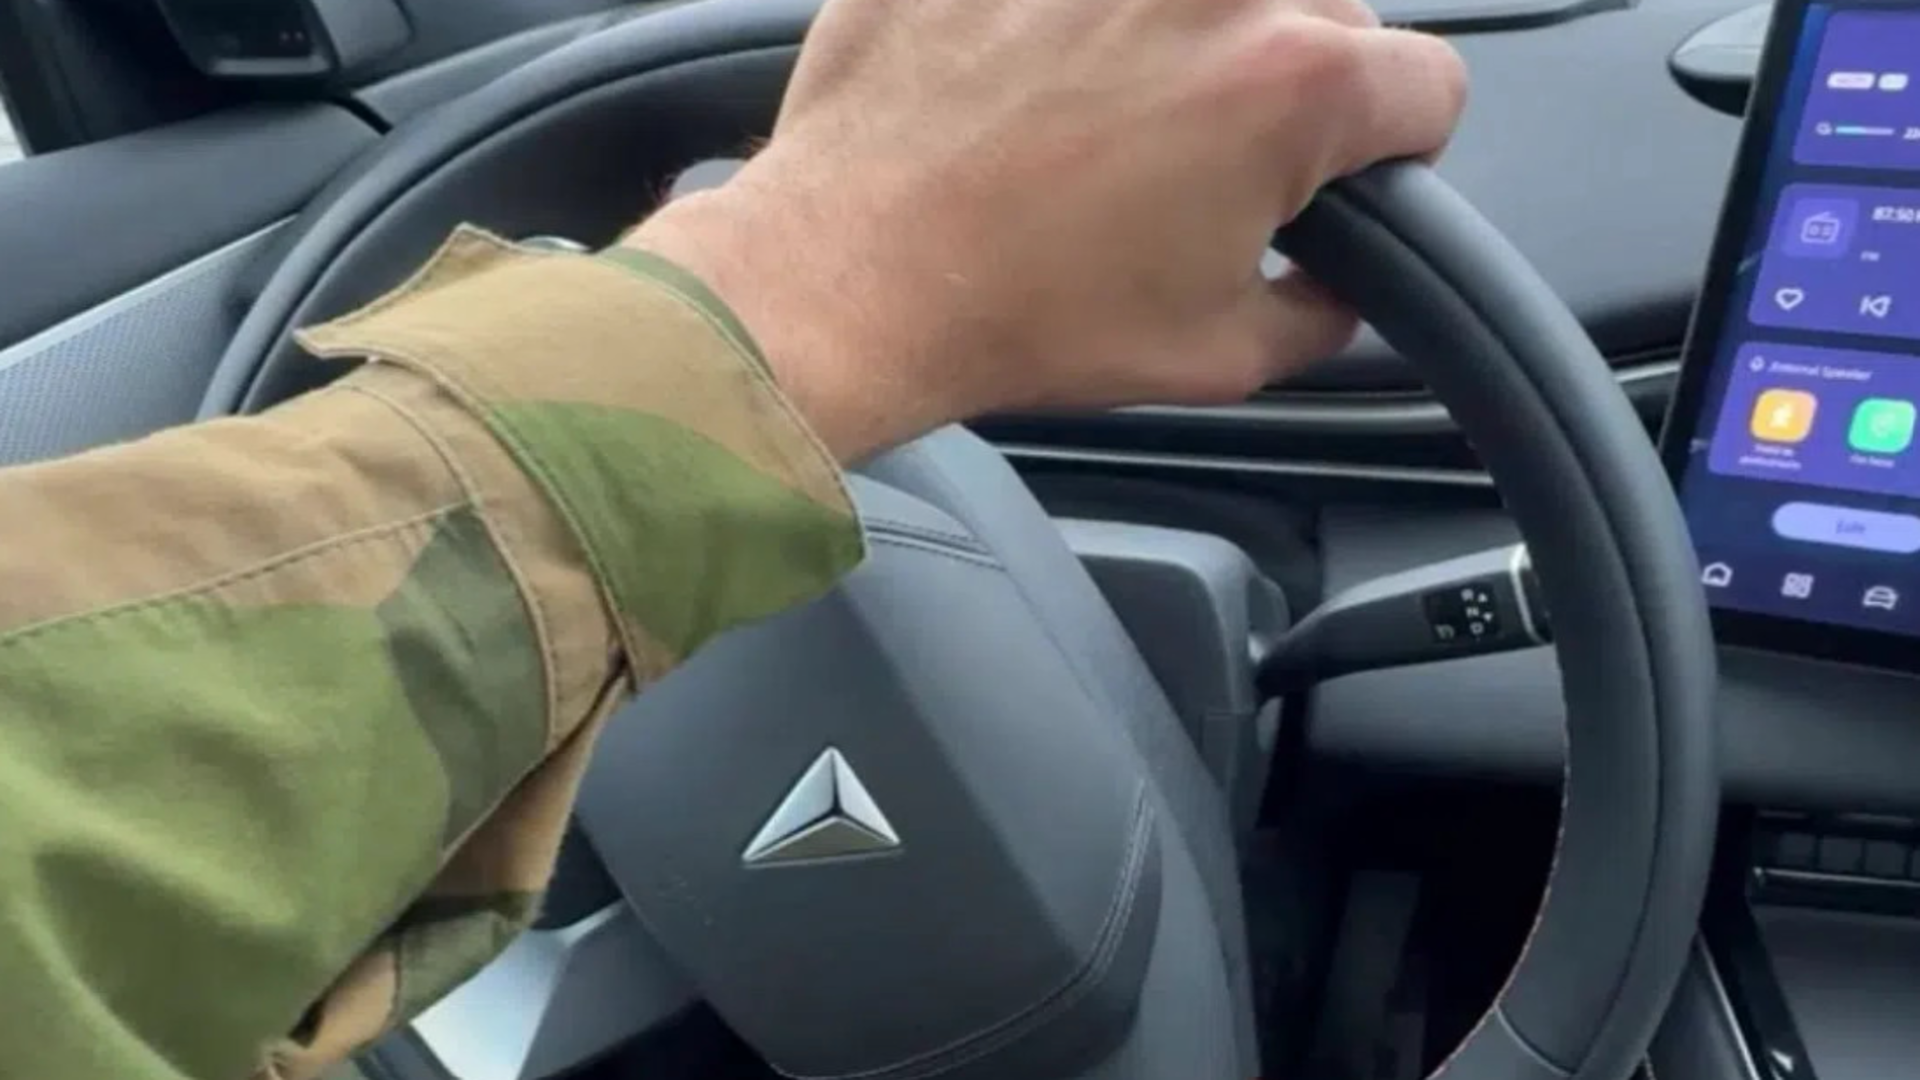
Dashcams captured soldiers entering vehicles, moving around, and typing security codesMilitary personnel deleted recordings after discovering them inside the rented carsA shortage of alternative vehicles kept the cars in military useRental cars used by the Norwegian army during an exercise in Oslo filmed soldiers and stored the recordings inside the vehicles without anyone noticing, reportts have claimed.The clips showed troops getting into and out of the cars, their movements and locations,…
L
Researchers uncovered a zero-click spyware campaign delivered through online advertisements, requiring no user interactionJournalists’ devices were infected with surveillance malware capable of stealing data, messages, audio, and videoInvestigation linked the operation to Israeli firms tied to ad-tech infrastructure and commercial spywareImagine this: You’re a journalist. You get to work, log into your computer, and go about your daily activities. While browsing the internet, you see an ad for…
L
Biomemory has unveiled DNA Shield, designed to provide offline, airgapped, secure storage of critical digital assets in synthetic DNAThe company foresees challenges to the resilience those assets (also known as “cold data”) and has hinted at the introduction of what it calls Molecular ITBiomemory is a co-chair of the DNA Data Storage AllianceCommercial DNA data storage company Biomemory has unveiled DNA Shield, a purpose-built synthetic DNA repository service that ensures critical digital…
L
Attackers exploited vulnerable devices to install legitimate bandwidth-sharing software and hijack internet connectionsCompromised systems were covertly added to proxy networks, enabling anonymous criminal activityCampaign affected at least 143 devices across 34 countries, highlighting patching and access-control failuresWhen threat actors break into a system, they don’t need to install malware to make use of the compromised endpoint - they can install perfectly legal, normal software, and…
L
Phishing campaigns are abusing calendar invites and meeting requests to steal Microsoft 365 credentialsAttackers hide malicious links in .ics files, fake meeting details, QR codes, and invite pagesResearchers observed hundreds of thousands of phishing emails targeting over 40,000 organizationsIf you get a calendar invite in your inbox be wary - it might be a carefully created phishing lure, designed to have you hand over Microsoft 365 or other login credentials.Security firm Check Point…
L
At the start of every school year, schools, colleges and universities across the UK race to onboard thousands of new students, faculty and staff members, provisioning accounts, issuing credentials and connecting a wave of new devices to institutional networks.That operational pressure creates opportunities for attackers, and this year, AI is amplifying the threat more than ever. Not only are phishing campaigns more convincing, but a hidden layer of unmanaged machine identities is expanding the…
L
KGB RAT is a malware-as-a-service platform offering remote access, credential theft, and crypto hijacking featuresThe malware includes unusual psychological tactics such as fake BSODs, jump scares, and screamer functionsResearchers found multiple operators using the tool, which is marketed as legitimate software despite its criminal capabilitiesHalloween is just around the corner, and cybercriminals are making use of it to give Windows users a good scare (and then some!) - ater all, few things…
L
Bank of America hired 1,000 contractors and spent hundreds of millions fixing AI-discovered vulnerabilitiesAnthropic’s Mythos uncovered enough flaws to trigger large-scale remediation across major banksFinancial institutions warn advanced AI security tools are exposing weaknesses faster than teams can patch themBank of America, one of the largest financial institutions in the United States, was forced to hire a thousand people on contractor roles, and spend north of a $100 million dollars to…
L
Microsoft helped dismantle a cybercrime marketplace that sold phishing tools, accounts, and scam infrastructurePlatforms CoGUI and Iron Man enabled large-scale phishing campaigns targeting organizations worldwideThe operation drove over a billion phishing messages before domains and thousands of accounts were seizedLate last year, Microsoft set out to investigate what seemed to be yet another phishing campaign. However, what it uncovered under the surface was a lot bigger - it was a sprawling…
L
For technology teams, connecting telemetry has traditionally been seen as a route to greater visibility. The assumption is straightforward: the more information available about what is happening across an environment, the easier it should be to understand problems and respond to them.But as modern technology environments have grown in scale and complexity, that equation no longer looks quite so simple and teams have found themselves dealing with fragmented telemetry and unclear signals. It now…
L
Two LiteLLM flaws let low-privileged users gain administrative control and execute malicious codeAttackers could also steal AI provider API keys through a server-side request forgery bugOrganizations should upgrade to LiteLLM 1.83.9+ and rotate potentially exposed credentialsSecurity researchers recently discovered two vulnerabilities in a popular AI gateway that allowed threat actors to take complete control of the system, steal sensitive files and AI provider API keys, and execute malicious…
L
Attackers reportedly accessed Denmark’s population registry through a third-party company using weak credentialsData on roughly 8.8 million individuals may have been exposed, including CPR identification numbersBreach highlights severe third-party security failures, with reports citing passwords like “123456”Data held by the Danish national population registry was allegedly protected by a very strong, very difficult-to-crack password: 123456. This claim was made by a person who allegedly broke…
L
Most people spend more time in their browser than in almost any other piece of software they use. It's where they read the news, check their bank accounts, work, shop and more. Yet, for something so central to daily life, most people have a surprisingly limited understanding of what their browser is actually doing behind the scenes.That gap was easier to overlook when browsers had a relatively simple job. They opened websites and displayed them on a screen. But today, browsers hold login…
L
Researchers found an exposed database containing 13.7 million records from past data breaches and leaksArchive included passwords, banking details, and data tied to major firms like AT&T and AmazonThe database was secured after disclosure, highlighting ongoing risks from exposed breach repositoriesIndian software development platform Vibetech seems to have been collecting data exposed in various leaks and cyberattacks and creating one big repository. Besides the questionable legality of the…
L
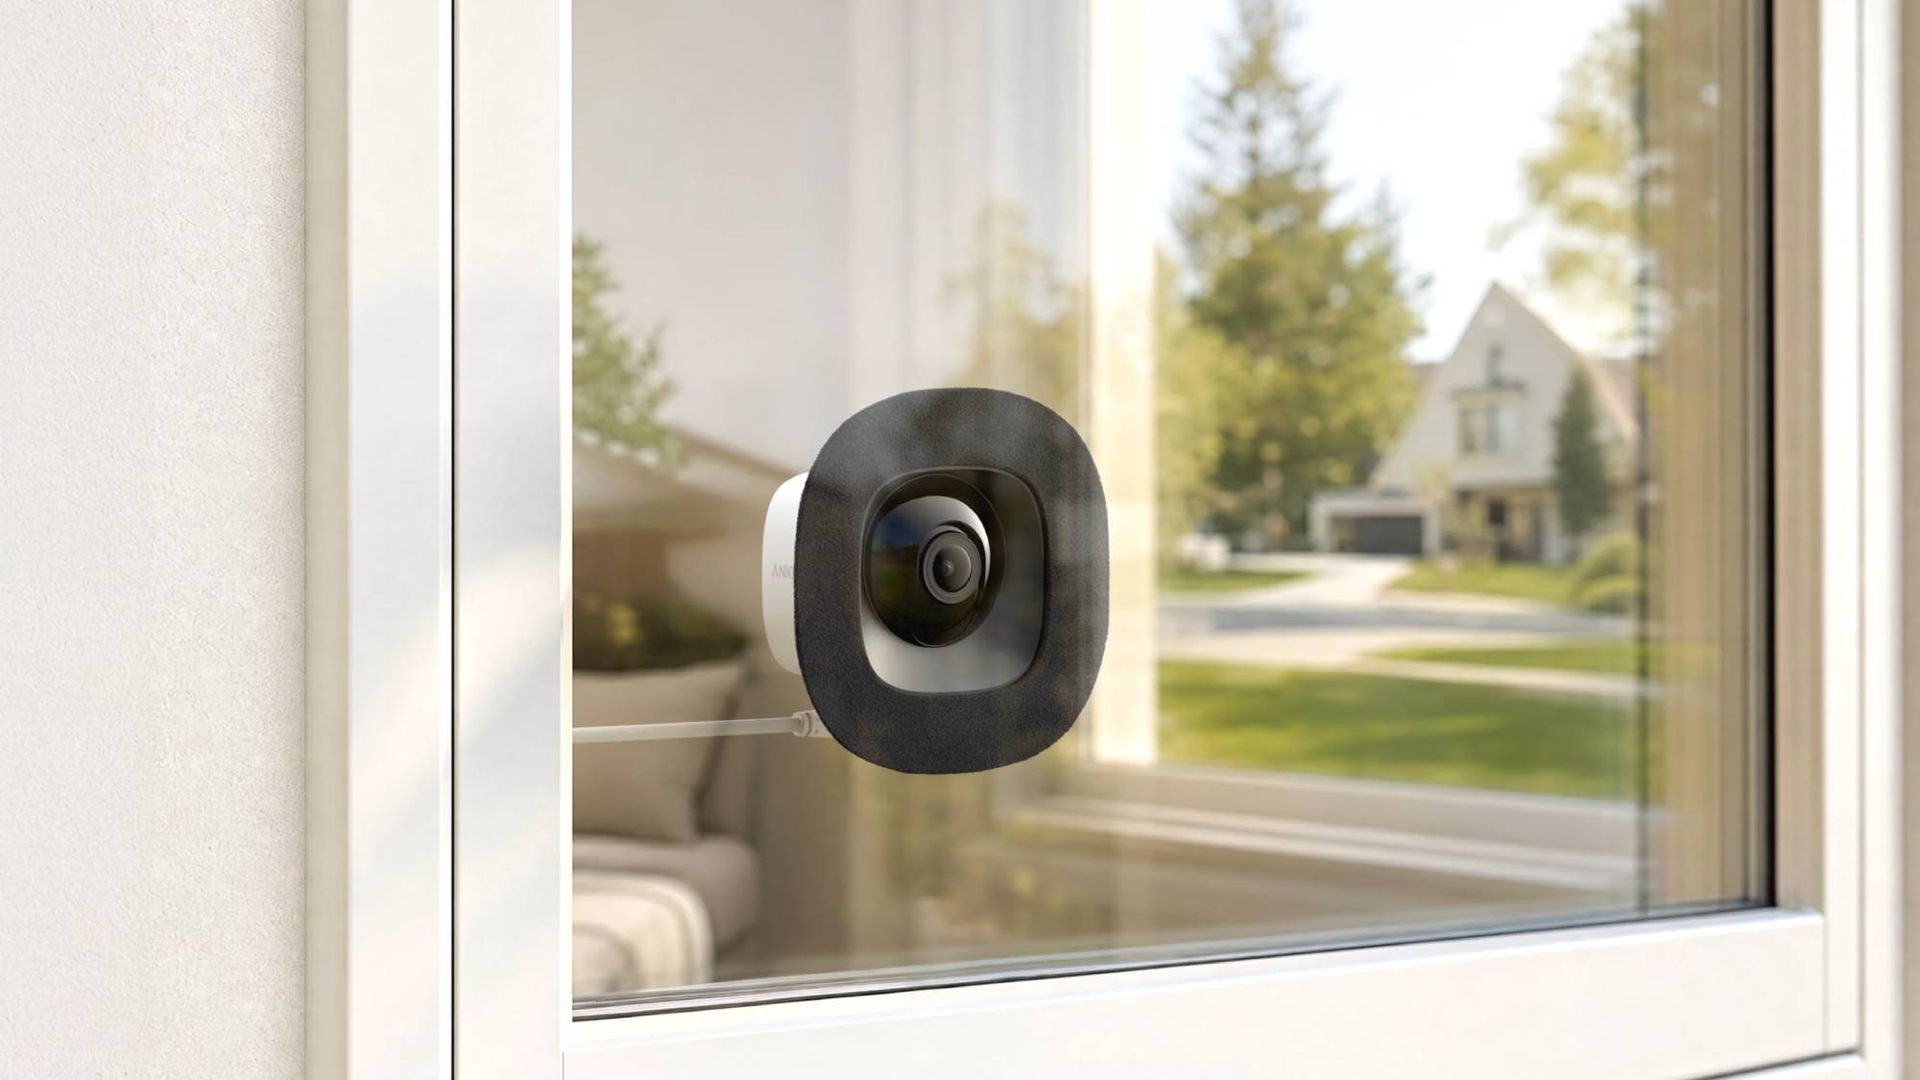
Eufy's new home security camera sticks to your window to let you monitor the outside view from inside It's $79.99 / £69.99, subscription-free, and offers 2.5K resolution The only drawback is its power cable, which might restrict where you're able to place itEufy’s new security camera isn’t just a small, handy smart home tool that removes the hard work from installing security devices in outdoor spaces — it’s also affordable and, crucially, subscription-free. Hot on the heels of the Eufy Video…
L
AI Scout tracks which artificial intelligence services employees actually use at workEmployees are increasingly turning to AI services outside approved channelsNordLayer AI Scout can warn, redact, or block sensitive prompts before submissionEmployees are increasingly using AI tools at work, including services their employers may not have approved or formally provided.That creates uncertainty about which AI platforms workers access, what information they submit, and how those systems connect…
L
Anthropic warns that self-replicating AI worms could become feasible by the end of the yearThese AI worms could hijack hardware ranging from IoT devices to data centersSmaller models are already capable of adapting to unfamiliar hardware and self-replicationAnthropic has warned self-replication could become feasible for small AI models on internet-of-things (IoT) devices in just a matter of months.This could be a big problem because a self-replicating AI model does not have a centralized…
L
Clicking 'Learn more' would skip Microsoft account demands when setting up Windows 11It now shows user data policies, so you'll have to sign in with your account (or create one)Having an account can make certain things easier, but it's one less choice for consumersMicrosoft has finally fixed one of the easiest ways for attackers to bypass its account requirements when installing Windows 11, but it's bad news for anybody who didn't want to sign in with – or create – a Microsoft account during…
L
Attackers exploited critical AhsayCBS backup software flaws to compromise organizations’ backup serversIntrusions deployed webshells and disguised XMRig cryptominers for persistence and stealthResearchers urge immediate patching, restricted access, and full system reimaging if compromisedIn a particularly brazen hack, threat actors were seen targeting the servers that businesses use as backups in case of a cyberattack. The vulnerabilities used in this attack have since been mitigated, but since…
L
Ahold Delhaize took systems offline after a cyberattack, though details remain limitedDisruptions affected employee services and customer-facing websites across multiple retail brandsCompany is investigating the incident amid concerns of another major ransomware-related attackAhold Delhaize has suffered a cyberattack that forced it to pull parts of its IT network offline.On October 12, 2026, the retail giant issued a brief statement, saying it is experiencing a “security issue” within its…
L
Malware infection at a third-party contractor may have exposed data of 8.7 million customers and employeesExposed records included personal details, though no payment data or confirmed misuse was reportedIncident highlights supply-chain risks, with Daiichi Kosho investigating and reviewing contractor securityEven the entertainment industry is not safe from data-stealing cybercriminals - Daiichi Kosho, one of the biggest entertainment system makers in Japan, has disclosed a malware infection in…
L
Mozilla wants security-conscious companies to use Firefox Enterprise"Choice is a lie," Mozilla CEO says, referring to browser enginesThunderbird Enterprise is also in the worksMozilla has introduced Firefox Enterprise, a brand-new version of its browser designed specifically for organizations that need extra security, governance and compliance controls.The company argues businesses have become increasingly dependent on a small number of tech companies, handing over certain levels of control to…
L
Discussions about passkeys replacing passwords as the go-to sign-in method have rapidly accelerated. The National Cyber Security Centre (NCSC) has acted as the catalyst for this transition, describing the shift as "overhauling decades of security practice". Finally, the industry has reached a collective point of recognition: traditional, static passwords are a weak defense against modern, automated threats.AI has turned cybercrime into a highly efficient, industrial-scale enterprise. With…