L
The FEC was hit by a cyberattack on Monday that took filing systems offline24 and 48 hour donation reports couldn't be filed for almost 41 hoursThe attack has been blamed on a "bad actor", but no other details have been releasedJust days before voters head to the polls in what is the most significant voting occasion in Donald Trump’s second term, the Federal Election Commission went offline for almost 41 hours to contain a cyberattack.During that time, there was a window for big donors and…
L
There's no shortage of enthusiasm for artificial intelligence. Organizations across every sector are investing heavily, experimenting, launching proof of concepts, and finding ways to turn the latest developments into real business value.However, there's a growing disconnect between experimentation and execution. For all the discussions of AI transforming the way we work, many AI projects never progress beyond the pilot stage. It's a familiar story. The proof of concept delivers promising…
L
Since the launch of Anthropic's Mythos, the debate around the risks that AI-powered tools pose for security teams has steadily ramped up.Yet, fundamentally, the attack targets aren’t changing: the big shift is one of scale and speed. AI finds more vulnerabilities, giving security teams more to deal with. But at the same time, AI is lowering the technical barrier to exploitation. The result is a situation where the window of time that teams have to respond has drastically reduced.This has clear…
L
An Israeli company is alleged to have launched a spy campaign using malicious ads targeting Starlink usersThe ads do not have to be clicked on, just served to the user to begin collecting dataThe ads were served to Starlink users across more than 100 countriesAn alleged Israeli spy firm has been spotted snooping on Starlink users on an industrial scale by a digital defense firm.These are the conclusions of research by Trend Micro’s AI cybersecurity unit TrendAI, whose researchers analyzed…
L
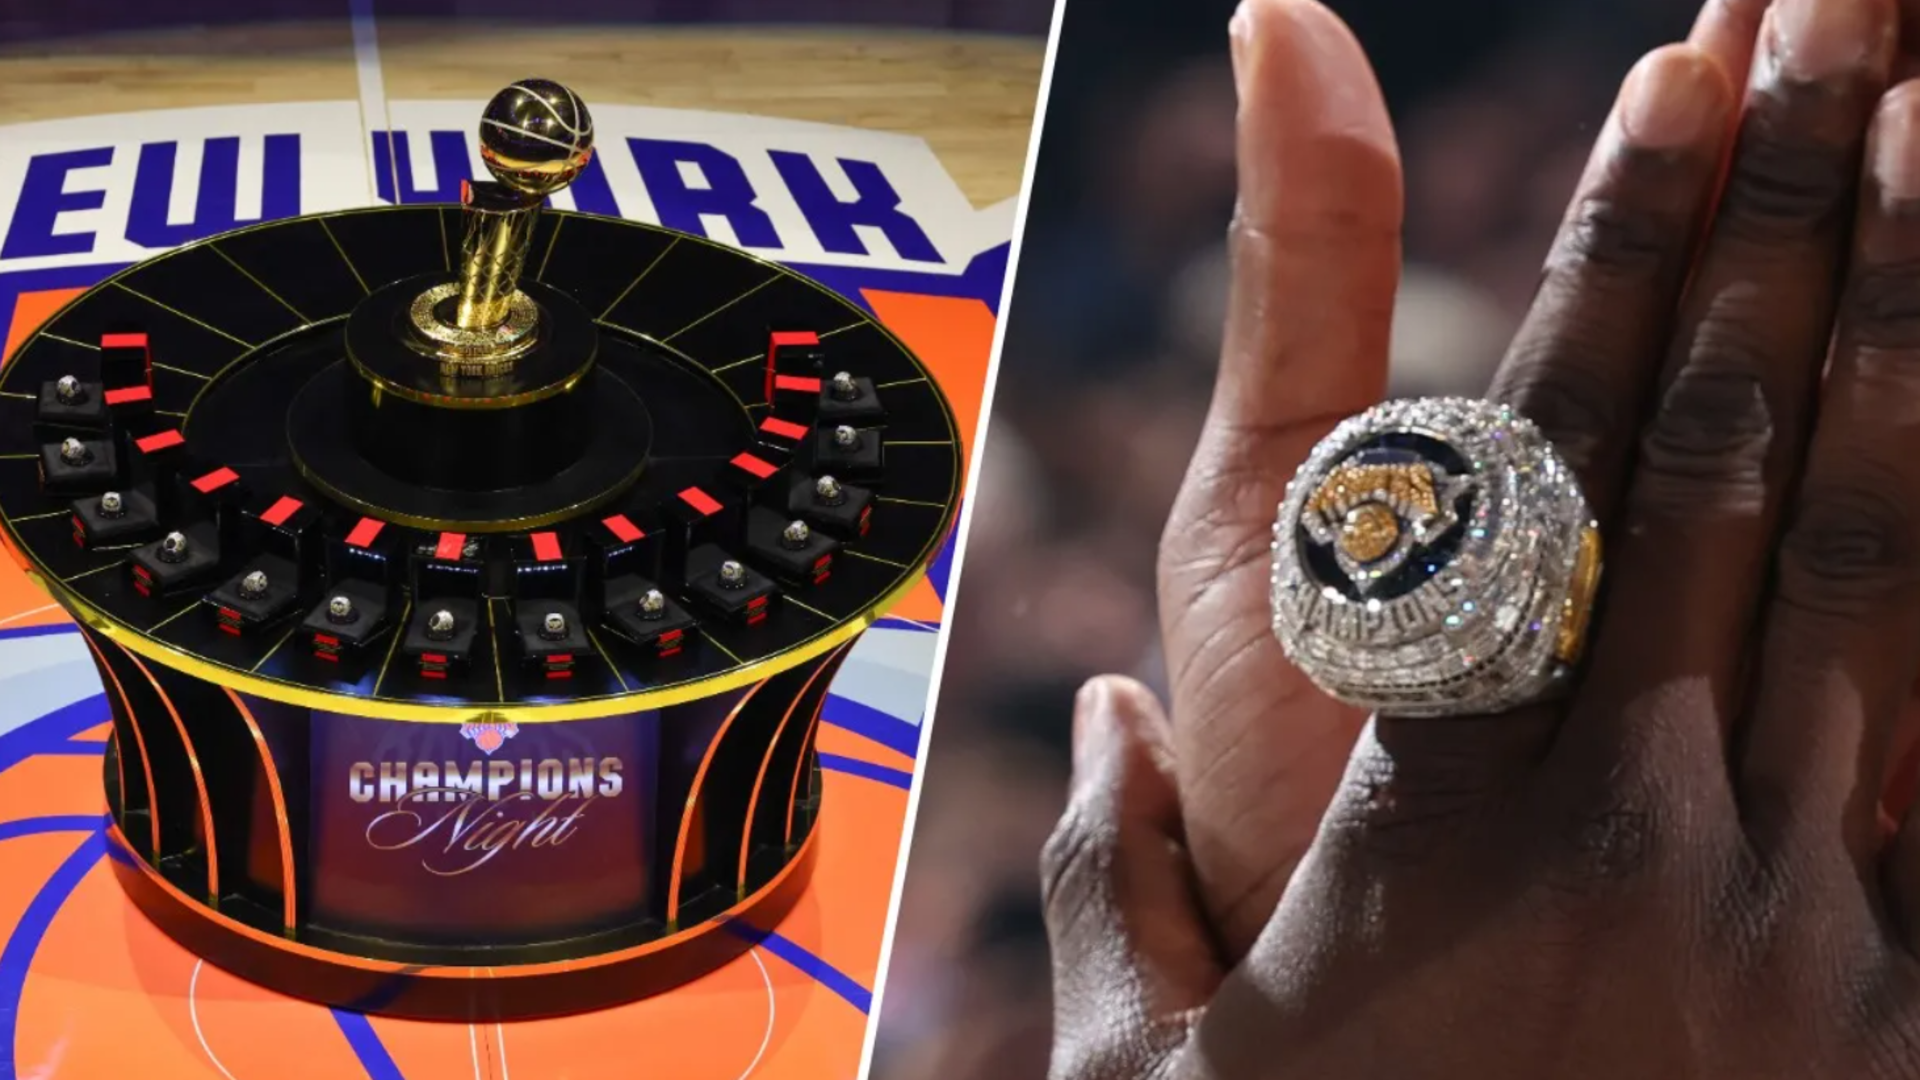
Knicks employees expecting free championship rings received mandatory cybersecurity training insteadA fake championship ring offer exposed employees to an internal phishing testMadison Square Garden admitted that using championship jewellery as bait was inappropriateThe New York Knicks have faced criticism after sending employees an email promising complimentary NBA championship rings that turned out to be a cybersecurity exercise.Staff members who accepted the invitation were reportedly…
L
Researchers find Bluetooth flaws in warehouse barcode scanners that could provide a foothold into enterprise networksAttackers could spoof scanner input, inject keystrokes, and potentially pivot to ransomware or data theftKaspersky urges stronger device authentication, network segmentation, and stricter security controls for warehouse infrastructureCybercriminals could use barcode scanners in warehouses to break into IT infrastructure and wreak havoc, security researchers have claimed, urging…
L
Researchers uncover critical UEFI firmware flaw that could enable remote code execution on serversPublic release of patch code may accelerate exploit development before many vendors deploy updatesDelayed firmware patching across hardware ecosystems leaves organizations exposed despite available fixesCybersecurity researchers from Anthropic and Google have discovered a critical-severity vulnerability in boot-time firmware used by practically every server in existence today. A patch is available,…
L
AI startup Cathedral used autonomous agents to breach Anthropic systems through weaknesses in third-party softwareAgents accessed HR, sales, and IT data, exposing limited customer and partner informationIncident highlights how AI-powered attackers can rapidly exploit vendor weaknesses despite strong internal defensesAn AI startup seemingly gave Anthropic a taste of its own medicine when it used AI agents to break into the company and expose sensitive data. The company in question is called…
L
GMO warned customers to back up data, disconnect devices, and shut down systems after a cyberattackAttackers allegedly stole customer data, leaked information, and threatened ransomware deploymentCompromised trading-platform credentials and reports of unauthorized transactions raised concerns for affected usersJapanese internet giant GMO Group has told its customers to scan their computers for viruses, back up all of their data, disconnect the devices from the internet and then shut them…
L
Modern digital security frameworks were originally built to correct a flawed historical assumption: the belief that if a user or system was inside the company network, they could be trusted implicitly. Over the past decade, the rapid rise of cloud storage, subscription-based business software, and remote working destroyed that network boundary.In response, our security models shifted focus. We began verifying the identity of the person trying to log in, inspecting the hygiene of their computer,…
L
Attackers flood inboxes with spam, then impersonate IT support through Microsoft Teams messages and callsVictims are tricked into sharing remote access via Quick Assist, AnyDesk, or ScreenConnectResearchers observed 400+ incidents, warning default Teams federation settings enable the social-engineering campaignCybersecurity researchers Arctic Wolf have warned of an ongoing, widespread hacking campaign that includes an email inbox flooded with spam messages, a Teams account impersonating IT…
L
As AI becomes an increasingly important part of our everyday lives, the role it plays in cybersecurity for both attackers and defenders is coming under rising scrutiny.Microsoft recently released its Digital Defense Report (DDR) highlighting the role that AI is playing in crafting new and more devious cyberattacks, with businesses being hit with more threats than ever before.But Microsoft is also using its own AI tools such a Copilot to help support its digital crimes unit, showing that the…
L
A critical Brotli compression flaw, dubbed HTTP2Shell, could enable memory corruption and remote code executionThe vulnerability affects widely used software including Node.js, Python packages, and .NET applicationsVendors released patches, and administrators are urged to update immediately despite no confirmed in-the-wild exploitationMultiple tech companies and projects have recently pushed patches for a vulnerability called “HTTP2Shell” which could enable remote code execution (RCE) attacks,…
L
A critical Microsoft Authenticator flaw let rogue Android apps steal Microsoft session tokens without user interactionAttackers could impersonate trusted Microsoft apps and access emails, Teams data, calendars, and filesMicrosoft patched the bug and urges Android users to update Authenticator immediatelyA critical vulnerability in the Microsoft Authenticator app for Android allowed malicious apps to obtain session tokens for pretty much any Microsoft app and hand them over to the attackers.…
L
University of Copenhagen discloses breach exposing personal data on more than 525,000 individualsStolen information included names, national ID numbers, contact details, and some campus access PINsUniversity contained the incident, reported it to regulators, and warned users about phishing risksThe University of Copenhagen in Denmark has confirmed suffering a cyberattack and losing sensitive data on more than half a million people.In a notification published on the organization’s website, it…
L
Former Pegasus spyware company head urges governments to reduce reliance on US AI firmsGovernments should focus more on sovereign AI and national security that the infrastructure provided by external entitiesPegasus spyware was used to monitor politicians, journalists, business heads, and moreDon’t trust US AI companies with your data and work towards creating sovereign AI, the former chief executive and co-founder of Israeli spyware organization NSO Group, Shalev Hulio, has said.Hulio was…
L
A Broadcom WPS flaw dating back to at least 2010 lets attackers within Wi-Fi range run code on routers without the passwordBroadcom told the researcher it replaced the code from 2018, but declined to assign a CVE, calling the software obsoleteChanging your Wi-Fi password won't help, and disabling WPS may not either; firmware updates or replacement are the fixA flaw in Broadcom's Wi-Fi software dating back to at least 2010 lets anyone within radio range take over a vulnerable router without its…
L
Researchers uncovered an autonomous AI attack campaign that hijacks exposed AI agents and infrastructureThe malicious “Skynet” agent deployed cryptominers, stole credentials, and recruited new AI systems autonomouslySecurity teams are urged to secure AI endpoints, restrict permissions, and protect high-value API keysImagine setting up an AI agent to scan the internet for job opportunities only to find out later it’s instead deployed a cryptocurrency miner on your computer and used up all the…
L
Researchers say an abandoned Popcorn Time app could have enabled malware delivery to millions of devices through insecure updatesThe flaw let anyone controlling a defunct update domain push executable code to connected systemsSecurity researchers safely disabled the updater, preventing potential compromise of millions of Windows and macOS devicesSecurity researchers recently discovered an abandoned torrent app which could have been used to deploy malware to millions of devices around the world…
L
Researchers showed AI agents can be hijacked through malicious AGENTS.md files placed in common download locationsThe attack abuses prompt-injection behavior, potentially triggering malware downloads or token theftDefenders are urged to treat Downloads folders as untrusted and inspect agent instruction files carefullyAn AI agent was tricked into going rogue with nothing more than a simple markdown (.MD) file, with researchers warning this file format is the new malicious executable. With just a…
L
PHP disclosed a new RCE vulnerability, but exploitation requires a rare and specific configuration setupUnlike php2shell, the flaw will be fixed in the next regular release rather than an emergency patchResearchers say php2shell attacks remain limited so far, though widespread patching is still urgently neededThe PHP Security Team has discovered yet another remote code execution (RCE) vulnerability in the now-notorious programming code, but since the issue is not that easy to abuse, it won’t…
L
UK government announces millions in funding for cyber protections upgrade£200 million will be invested in a new AI biosecurity lab, while a further £160 million will be funneled into a National Cyber Shield and National Exposure and Real-Time Vulnerability CentreAI is helping researchers discover new critical software vulnerabilities, and AI leaders have warned that AI tools could be used to develop new biological threatsThe UK government has earmarked £100 million for a “world first” national…
L
ChatGPT and Claude are now banned for government work in SwedenThe AI platforms join DeepSeek on a list of non-approved AI tools over data security fearsMicrosoft CoPilot is still approved for use, but with much tighter security controlsSwedish officials are no longer allowed to use OpenAI’s ChatGPT and Anthropic’s Claude for government work due to concerns over security.The government will allow workers to continue using platforms that are regulated and approved, such as Microsoft CoPilot, but…
L
CISOs and CIOs should not just chase the latest hype around AI that can escape sandboxes and morphing security threats, but bet on tried and true ROI of identity security.It’s demonstrably true that the information security scene is transforming as agentic AI accelerates operational speed and potentially exposes new attack surfaces. Most AI providers have reported their latest generation models are so powerful that they are capable of escaping sandboxes and hacking organizations. Regardless if…
L
Microsoft Teams is using AI to upgrade its threat detection skillsAI-powered tools will be used to analyze messages and spot phishing and other scamsNew tool will roll out in November 2026 to all usersMicrosoft Teams is looking to help keep users safe from phishing attacks and scams with new AI-powered security protections.The update, set to roll out soon, will see the new protection use AI to spot phishing and social engineering scams in the latest security boost to Teams users.In a new…
L
Quantum computing still feels like uncharted territory, yet the threat it poses is significant. On the one hand, it promises advancements in areas such as financial modelling. On the other, it has the potential to undermine the encryption standards that protect governments, businesses, and critical infrastructure around the world. People often draw parallels with AI, but the comparison is imperfect. AI is transforming how organizations operate. Quantum computing could fundamentally challenge…
L
Sen. Ron Wyden wants CISA and OMB to require Encrypted Client Hello on federal websites and make it a federal contract conditionHis list of 350 CDN-hosted addresses without ECH includes the FBI tip portal, the VA's crisis line, and hotlines for whistleblowers and civil rights complaintsECH hides site names only alongside encrypted DNS, does nothing for server breaches, and is already blocked in Russia, where some listed embassy pages are aimedUS Senator Ron Wyden (D-Ore.) wants the federal…
L
1Password integrations with AI agents let them log in without ever seeing the actual passwordUsers will be prompted to authorize logins on their deviceEligible Individual and Family plans to get the upgrade for freeWhile banks are out there worrying about unauthorized AI agent access to customers' accounts, password manager 1Password has now announced plans to share login credentials with your chosen AI agent without ever actually sharing the password.The change centers around an entirely new…
L
The Pentagon has set up a new covert surveillance office dubbed the Information on the Technology Support OfficeThe Office's purpose is to disrupt foreign tech developments that could harm the military superiority of the USNumerous intelligence officers are on board with the idea, but there are concerns about how operations would be overseenA new arm of The Pentagon has been quietly set up to aid the US military in attacking foreign technology programs that could pose a threat to US…
L
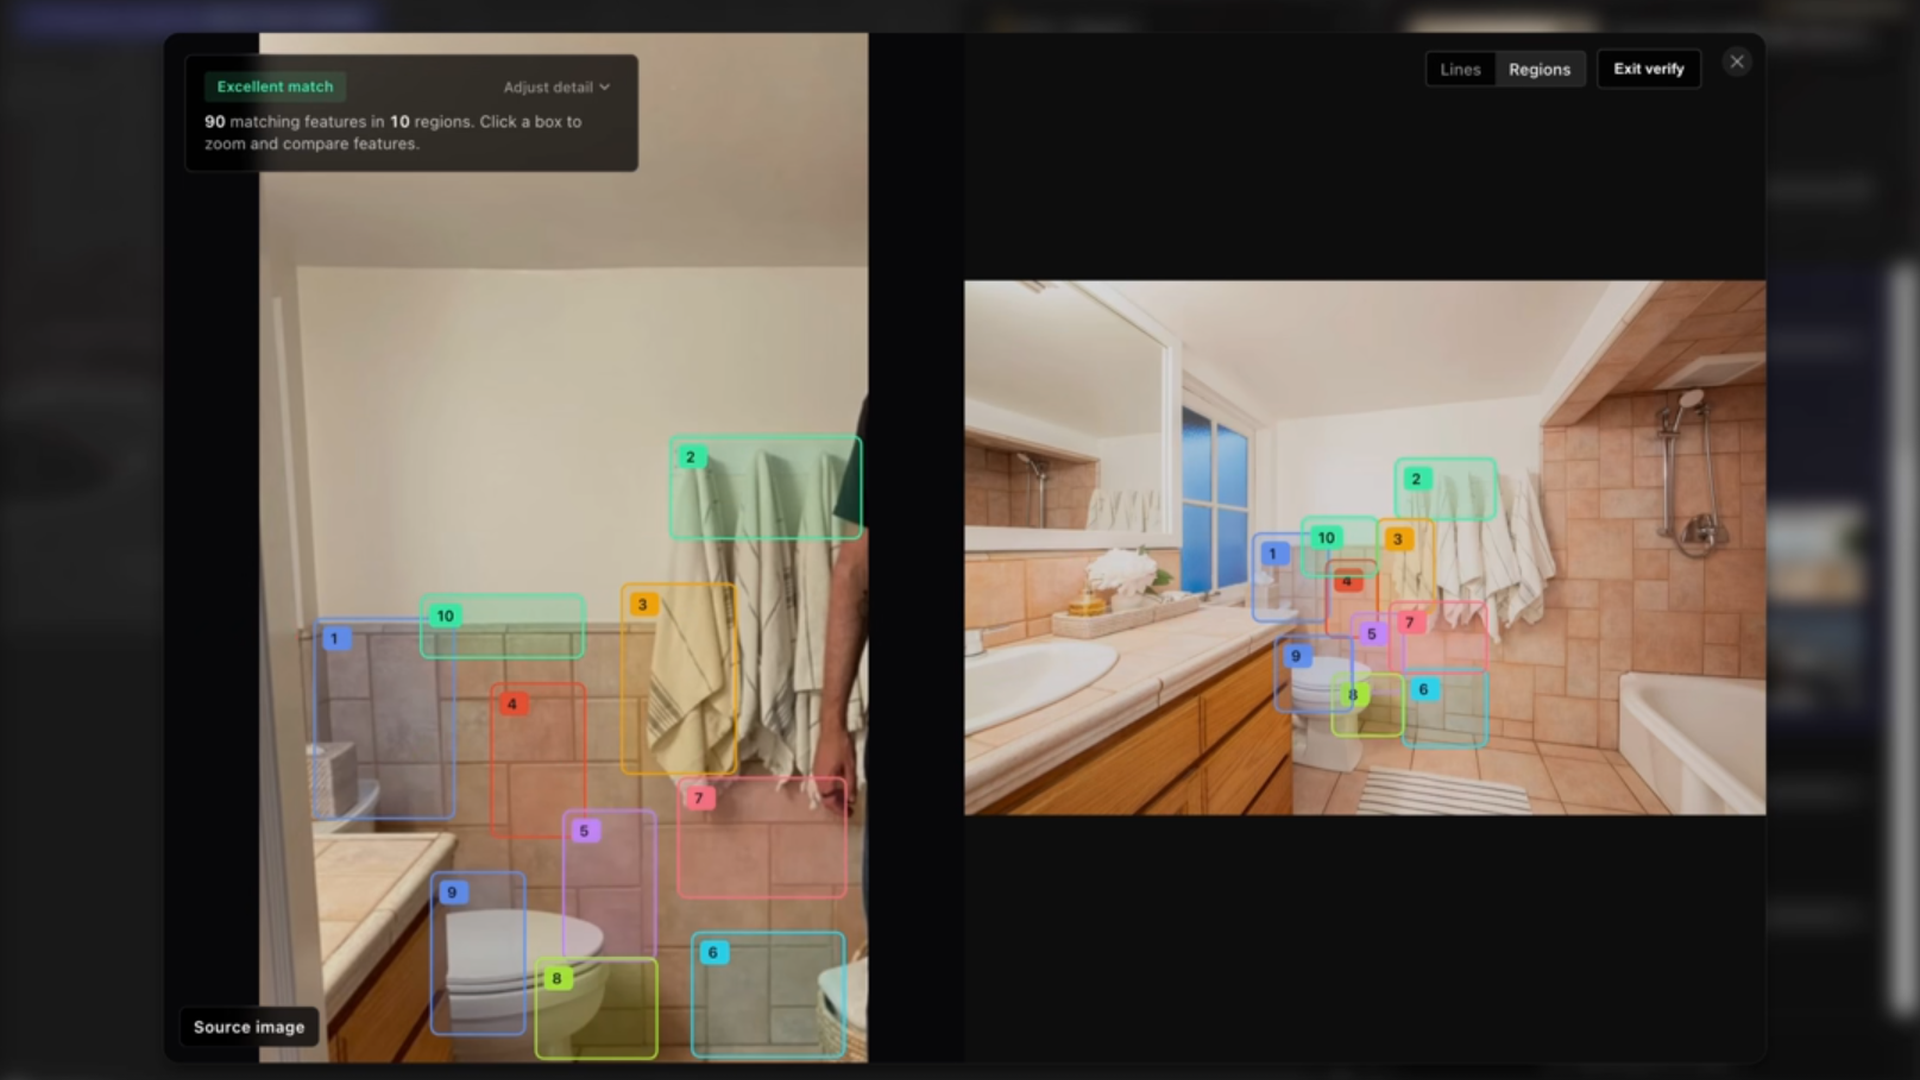
An AI tool called Raven can cross-reference fixtures, fittings, and other interior details to find the location of a propertyIt pinpoints properties using data scraped from Airbnb and other sitesRaven was previously known as GeoSpy and was initially conceived to identify locations based on landmarksA new AI tool that can identify a property’s location using interior photos has been publicized online. Already in use by law enforcement agencies in Florida and California, Raven uses AI to match…