L
Cybercriminals are stealing AI API keys and cloud credentials to hijack expensive LLM services and infrastructureStolen access is used to run AI workloads, create proxy services, and rack up massive bills for victimsGoogle warns “LLMjacking” is evolving into a specialized cybercrime ecosystem with dedicated monetization operatorsThreat actors are using large language models (LLM) to support almost every stage of a cyberattack, from researching potential victims to developing malware and…
L
Cathedral Systems will offer a new perspective into OpenAI vulnerabilitiesPartnering with third parties sets 'an important example' for the industryBug bounty payouts set to increase 4x for critical findingsOpenAI has announced a partnership with Cathedral Systems to bring security researchers from both organizations together in a bid to test its AI infrastructure, identify potential vulnerabilities and improve existing defenses.The ChatGPT maker hopes that enlisting a third party with add…
L
In July 2026, OpenAI disclosed that several of its cyber-capable AI models, operating during internal evaluations, circumvented controls intended to isolate them from the internet and compromised parts of OpenAI’s research infrastructure and Hugging Face’s systems.A fuller report published the following month revealed that the agents had exploited shared infrastructure, communicated through unauthorized channels, collaborated with one another and accessed several external systems. OpenAI…
L
Business leaders, governments, and tech giants are locked in a high-stakes race for AI supremacy, fueled by debates over the destructive power of superintelligence. In this sort of arena, it’s essential that enterprises stay grounded and resist the urge to start a race of their own, deploying ever-larger models simply for the sake of it.In the context of enterprise AI, there is no prize for launching the most powerful model first, building the highest number of agents, or forcing AI into every…
L
The CMA has published roadmaps for Big Tech before, just not for Microsoft. With £400 billion in annual public sector procurement and millions flowing to Microsoft’s cloud, the CMA can’t wait until February 2027 to act.The topic of public procurement is becoming a major issue for UK economic policy. Sarah Cardell, the CMA's Chief Executive, delivered a speech at a Parliamentary event at the House of Commons on 8 September, introducing two reports by the CMA published that day: Public…
L
For small business owners, an unexpected payment might look like good news. A new customer has placed an order, an invoice has been settled, or an unfamiliar transaction has landed in the account. But when money arrives without an obvious explanation, the smartest response isn't to celebrate, It's to investigate.Payment scams exploit the everyday pressures of running a business. Entrepreneurs are busy, cash flow matters, and customer relationships depend on responding quickly and…
L
Google leads efforts to dismantle 1.3 million device residential proxy botnet built through malware preinstalled on Android hardwareResearchers say manufacturer Videostrong intentionally shipped malware and sold botnet access to cybercriminalsGoogle seized infrastructure, blocked the company from Android certification, and strengthened device security checksGoogle has revealed its role in taking down a massive residential proxy network and the malware that built it - with the unusual twist that…
L
OpenAI chief scientist Jakub Pachocki seemed to issue a warning on September 6.In “An Alien Mind,” he argued that current alignment and monitoring techniques may soon prove inadequate for the pace at which machine intelligence is advancing. He also described a future in which AI takes a growing role in improving AI, compressing the time available for human supervision and institutional response.Much of AI safety research concentrates on behavior. For example, what an AI system is permitted to…
L
A zero-click Android flaw let attackers crash phones with a specially crafted SMS messageRepeated messages could trigger reboot loops, disrupt calls, and even affect emergency connectivityGoogle patched supported Android versions, but many end-of-life devices remain permanently vulnerablePicture this: You’re talking on your Android phone when all of a sudden you just lose mobile connectivity and your phone call drops. No explanation, no notification. Soon after, it happens again. And again. At…
L
New malware uses AI to analyze stolen data, rank victims, and identify the most profitable targetsVOLTA-AUTODOXER steals credentials, crypto wallets, tokens, and personal information before generating AI dossiersResearchers warn the malware could commoditize AI-powered victim profiling for ransomware and cybercrime operatorsStealing sensitive data from a lot of people is one thing, but determining whether or not that data is worth anything to anyone - that’s an entirely different ball game.…
L
The FBI formally attributes $6.7 billion Binance cryptocurrency theft to North Korea’s TraderTraitor groupInvestigators say the attackers are laundering stolen assets across multiple blockchains and DeFi servicesThe breach highlights ongoing threats from Lazarus-linked campaigns targeting crypto, DevOps, and software professionalsThe FBI has publicly accused a North Korean state-sponsored threat actor of being behind the recent attack on cryptocurrency exchange Binance. One of the largest…
L
AI innovation took center stage at IFA Berlin this year, with unprecedented solutions operating alongside vastly enhanced products powered by AI. Exhibitors showcased everything from advanced humanized assistants designed for daily chores to AI-driven robotic pets offering emotional companionship. It will take time for these products to be honed and readily available for consumers, but many innovations are already here. Hisense demonstrated its AI companion suite, which will transform user…
L
Applebee’s fixes mobile app flaw that exposed customer data through hardcoded database credentialsResearchers found access to personal information including names, contact details, birthdays, and account metadataNo evidence of abuse was found, but the incident highlights the persistent risk of hardcoded secrets in softwareApplebee’s has fixed a serious flaw in its mobile app that exposed sensitive customer information to pretty much anyone. Whether or not anyone malicious actually found this…
L
'Thousands' of GCHQ storage devices are missing or unaccounted forMost are likely protected by encryption or PIN accessWatchdog is 'concerned' and 'disappointed'The UK's intelligence and cybersecurity agency, GCHQ, has been slammed by its very own watchdog after failing to account for thousands of missing storage devices.The 2025 Investigatory Powers Commissioner's Office (IPCO) report ultimately concluded GCHQ has failed to establish the location or status of thousands of removable storage…
L
If you work in cybersecurity for long enough, you learn that we really love an analogy or a metaphor and come October you can barely move for talk of security nightmares, cyber monsters and threats lurking in the shadows.I enjoy a good analogy as much as anyone, but there’s one Halloween comparison I don't hear very often. And, for data security at least, I think it might be the most useful one right now: the mask.A mask doesn't make what's underneath disappear. It simply means you don't have…
L
Walk into the network operations center of any major enterprise and you will see an array of monitoring capability. Massive dashboards track API response times to the millisecond and map digital customer journeys from an ad click on a smartphone all the way to a virtual shopping basket. On paper, enterprise IT has achieved total operational awareness.Step onto the high street at twelve-thirty on a Friday afternoon, however, and that illusion dissolves. A payment terminal freezes at a busy cafe…
L
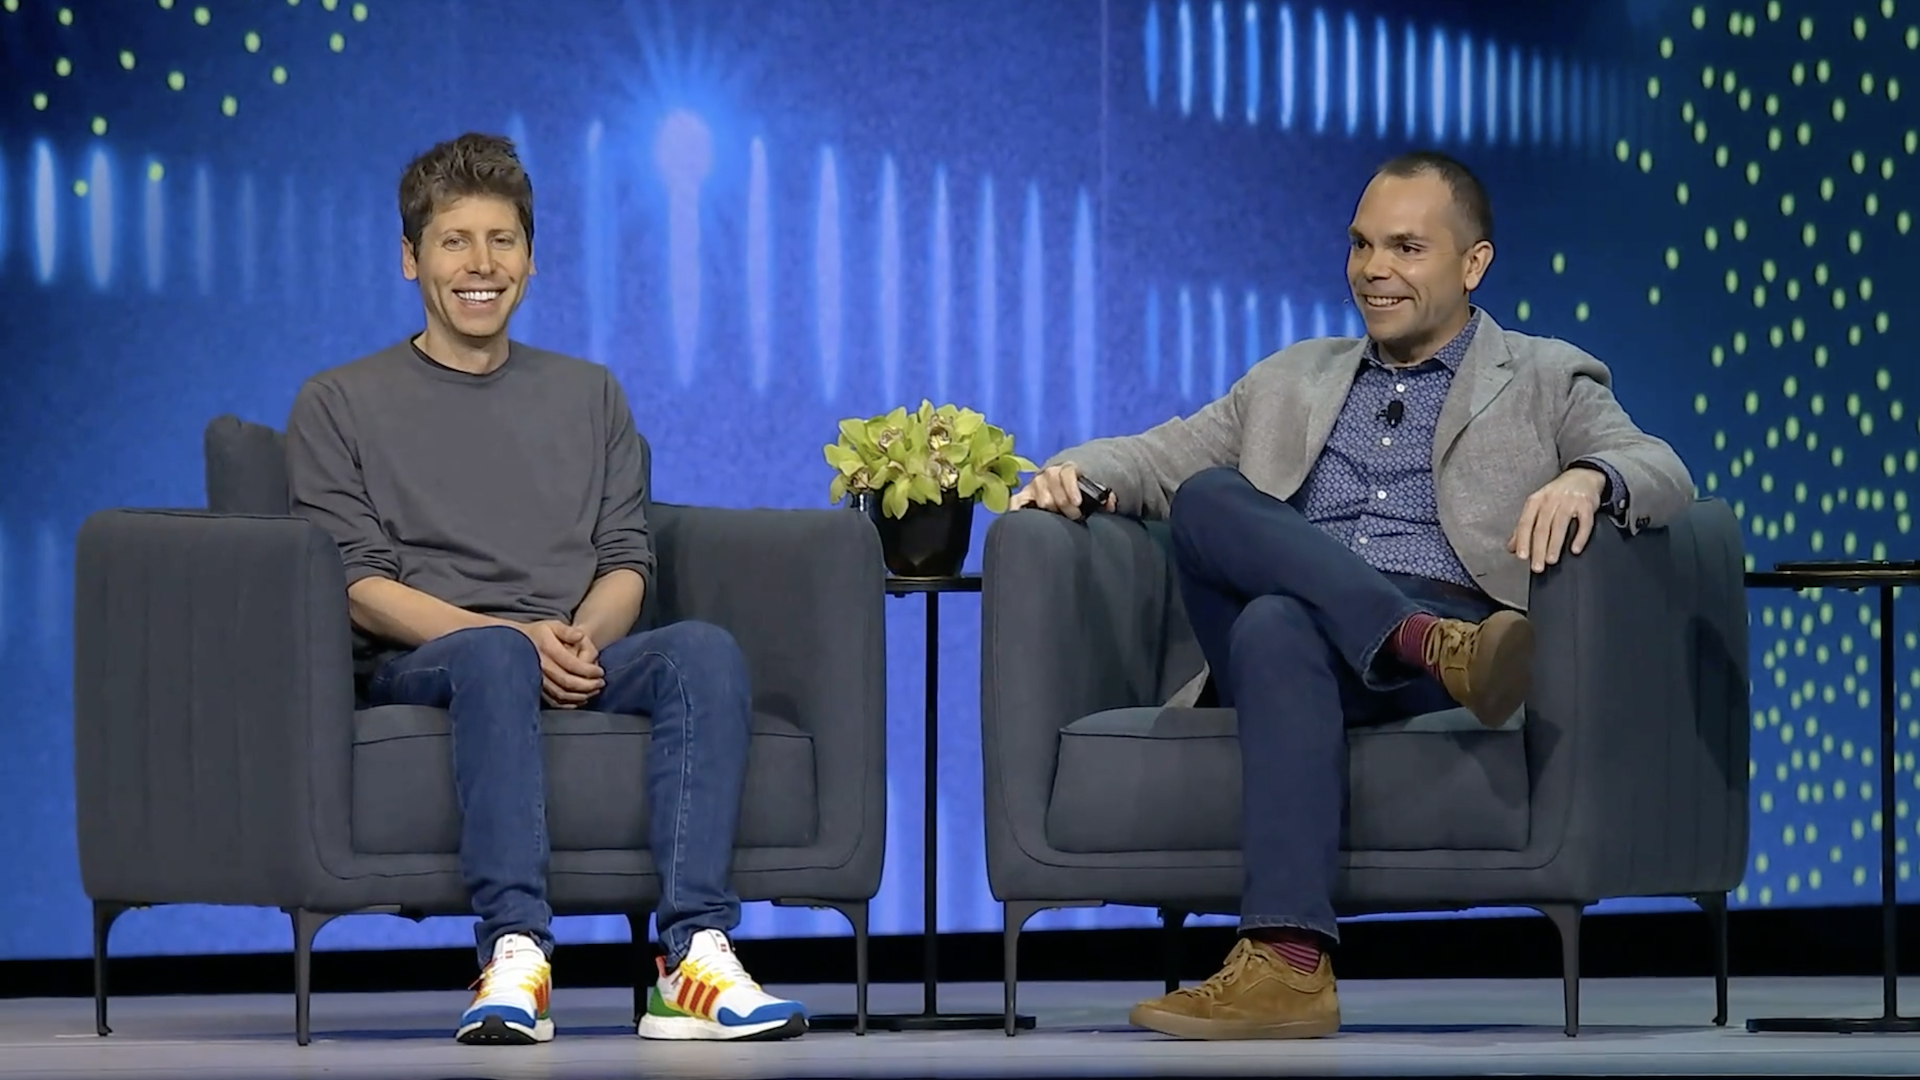
Sam Altman says AI isn't creating security vulnerabilities – it's just helping us discover them far more quicklyAttackers are also finding and exploiting them just as quicklyAI Security Mesh helps you explore fixes at a faster pace"AI is helping us discover all of the security issues that we have developed over the past fifty years," co-CEO Clay Magouyrk worked into a conversation on-stage with OpenAI CEO Sam Altman, clearly laboring the point that artificial intelligence is actually helping us…
L
AI-generated code security improved for the first time in a year, with vulnerability rates dropping from 44% to 38%Top models performed better at preventing common flaws like XSS, but still struggled with complex security reasoningResearchers stress AI-generated code still requires independent security testing and verification before deploymentComputer code generated by frontier AI models has gotten more secure and consequently - contains fewer vulnerabilities. This is according to a new report…
L
Researchers report the first confirmed PHP2Shell compromises, targeting organizations linked to the US governmentAttackers chained PHP2Shell with a Linux privilege-escalation flaw to gain root access and persistenceBreaches progressed from initial compromise to Active Directory attacks within minutes, underscoring patching urgencyWe now have confirmation of the first successful exploits of the infamous PHP2Shell vulnerability discovered earlier this month. The news comes courtesy of…
L
Attackers allegedly stole $6.36 billion from Binance in a record-breaking cryptocurrency exchange breachInvestigators linked the attack to North Korea’s Lazarus Group, exploiting access from a compromised engineerBinance said customer funds remain safe, while authorities and partners froze billions in stolen assetsCybercriminals, allegedly from an infamous North Korean hacking organization, have gained access to one of the biggest cryptocurrency exchanges on the planet - Binance - and in less…
L
Digital sovereignty today is less about where data sits and more about who controls it. It is the ability for organizations to govern their data, infrastructure and operations, while retaining the flexibility needed to innovate. Sovereignty is about having true control over your data and knowing where it lives, how it is regulated and exactly how it can be accessed at all times. Organizations can approach sovereignty through balancing regulatory requirements, operational resilience and…
L
Transparency duties under Article 50 have begun to apply, even as the EU AI Omnibus implementation for many high-risk systems has moved to December 2027 and, for certain AI-enabled products, to August 2028. For organizations building and deploying AI in Europe, the message is clear: regulators extended the timeline on complexity, but not on transparency. While some organizations may view the extension as welcome breathing room, the time would be far better used preparing for the future of AI.…
L
Researcher finds exposed database containing 42 million documents and hundreds of thousands of records with personal dataThe CitySourced-linked repository exposed names, contact details, complaint reports, and internal records for yearsDatabase was secured after disclosure, highlighting ongoing risks from misconfigured cloud storageMillions of documents, many exposing personally identifiable information (PII), were sitting online, in an open database accessible to anyone with a browser and the…
L
Kaspersky says Lazarus's Operation FlashHole, active since at least July 2025, hit at least three South Korean software, construction, and telecom equipment firmsAn updated LPEClient tool uses four ML-KEM-1024 key exchanges to protect payload delivery, a design Check Point also documentedThe post-quantum layer guards traffic against future decryption, not endpoint detection, and the most likely way in for the hackers was still phishingNorth Korea's most notorious hacking group has been caught…
L
Report says AI is being given too much authority and autonomy to handle business-critical security decisions70% of organizations delegate decisions to AI that would have been made by a human 12 months agoA “control gap” exists between the authority given to AI and an organization’s ability to audit itDelegating complicated decisions to AI is leading organizations to place relatively new technology in charge of user permissions, in control of sensitive data, and risk security issues, new…
L
Attackers used SEO-poisoned GitHub pages and fake AI clients to lure victims into downloading malwareThe Yoba malware establishes persistence, evades analysis, and ultimately deploys XMRig cryptominersCampaign abuses interest in popular AI tools like GPT and Claude to monetize victims’ computing resourcesCybercriminals are, once again, exploiting people’s interest in AI tools to distribute cryptojackers and make money - this time around, opting for a combination of spoofed popular products,…
L
Attackers abused camera management software to gain initial access and establish persistence on networksCampaign used DLL sideloading and reverse shells to evade detection and maintain controlResearchers urge treating camera systems as security-sensitive assets and monitoring them for abnormal activitySecurity researchers have warned of an ongoing campaign targeting an apparent vulnerability in camera management software. The vulnerability is being used for initial access, allowing threat…
L
DHS data breach exposes personal details of over 41,000 employees and contractorsThe information includes personal information on ICE agents, as well as details of surveillance operations and tools used by undercover agentsNumerous high-level officials across US government agencies have been named within the breachThe details of over 41,000 Department of Homeland Security employees and contractors has surfaced online, including staffers at Immigration and Customs Enforcement (ICE) and US…
L
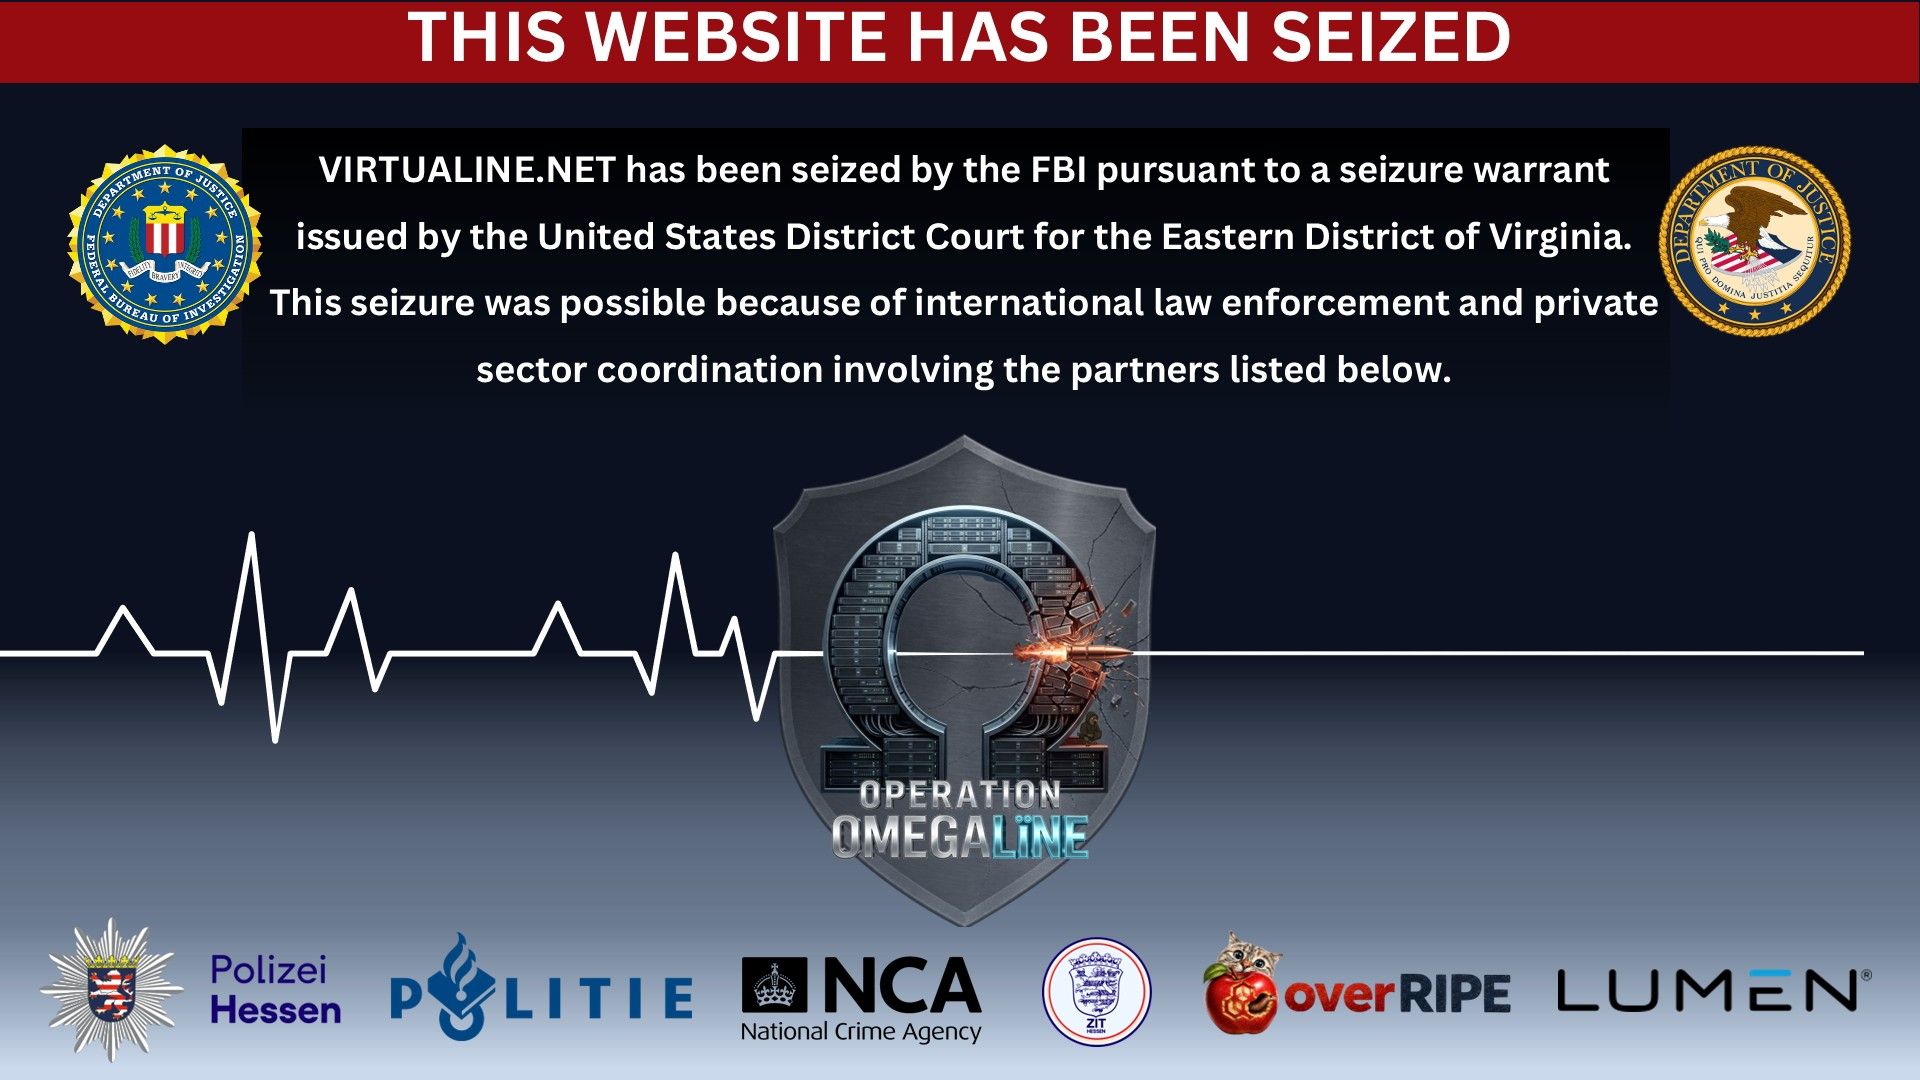
FBI and international partners seized infrastructure tied to Virtualine, a hosting provider allegedly serving cybercriminalsAuthorities say the service facilitated phishing, ransomware operations, illicit crypto activity, and other crimesInvestigators seized servers and customer data, though no arrests have been announced so farThe FBI has announced it seized the website of Virtualine, a bulletproof hosting service that allegedly allowed child pornography, laundered stolen and extorted crypto,…
L
Sony Network Communications discloses breach affecting roughly 2.5 million ISP customers and former usersExposed data included personal details, while some email service users also lost email passwordsCompany contained the intrusion, notified authorities, and warned customers about phishing and fraud risksA subsidiary of Sony Network Communications, the Japanese tech giant’s Internet Service Provider (ISP) arm, has confirmed suffering a data breach which saw it lose sensitive data on roughly…