L
Researchers found an exposed database containing more than 150 million Kik profile images, including around 75 million original photosExposed images were publicly accessible online and included content involving minors, prompting reports to child-safety authoritiesDatabase was secured after disclosure, but questions remain about exposure duration and potential prior accessKik, a popular American instant messaging app, was leaking profile pictures on the clearweb, putting even children and young…
L
Attackers compromised Optimizely and injected malicious JavaScript into more than 100 popular websites through a trusted content delivery pathThe payload stole cryptocurrency, harvested payment-card data, captured user information, and targeted iPhone visitors with exploit kitsOptimizely removed the malicious code, revoked access, and patched the signup-flow vulnerability used in the attackThreat actors broke into Optimizely and used it to deploy malicious code to more than 100 popular websites…
L
Infoblox is investigating a supply-chain breach in which attackers allegedly used a vendor’s access to steal employee and customer dataExposed information reportedly includes employee personal details and customer network configuration backupsCompany is offering identity protection services and warning affected individuals about phishing and fraud risksInfoblox has said it is currently investigating reports of a cyberattack and sensitive data theft. Initial reports describe it as a third-party…
L
Weak passwords like “123456”, “admin”, and “12345678” remain among the world’s most common choicesResearchers warn popular sports stars, games, and internet trends are also frequently used and easily crackedPassword managers, passkeys, and multi-factor authentication remain the best defenses against account compromiseWe’re just over a month away from 2027 and people still choose ‘12345678’ as their password for some reason.This is according to NordPass’ latest (and utterly depressing) report on…
L
Cereal malware secretly searched Romanian government emails for NATO and EU connectionsESET discovered previously undocumented software linked to Russia's Turla hacking groupHackers exploited Microsoft Exchange systems to conceal their email collection activitiesCyberespionage hackers allegedly linked to Russia infiltrated the Romanian government email servers, seeking correspondence involving NATO and European Union institutions.The operation relied on previously unseen malicious software ESET…
L
Hackers exploited exposed GeoVision surveillance systems to gain access to corporate networksAttackers manipulated Windows settings to interfere with Microsoft Defender protectionsCompromised computers were turned into cryptocurrency mining machines using XMRigHackers have exploited internet-accessible surveillance systems to infiltrate corporate networks, disable security protections, and install cryptocurrency mining software on compromised computers.The attacks abused GeoVision webcam…
L
Uber discloses third-party breach that exposed driver data, including driver’s license information for thousands of individualsThe incident stemmed from a compromise at AI infrastructure provider Fireworks, which was also targeted in broader LLMjacking attacksUber is notifying affected users and offering identity theft and credit monitoring services while investigations continuePopular ride-hailing service Uber has confirmed it lost sensitive data after one of its third-party service providers…
L
TSMC confirmed employee data was exposed through a third-party cloud provider rather than its own systemsStolen records reportedly include employee personal and banking information, with around 46,000 records offered for saleCompany is notifying affected personnel and investigating the breach alongside authorities and security expertsTSMC, the world’s largest semiconductor manufacturer, has confirmed suffering a cyberattack and losing sensitive files after a threat actor offered a large…
L
Osaka City disclosed exposure of 1.08 million email addresses through the wider Arara email platform breachStolen data included addresses used for government notifications, account activity, and administrative servicesOfficials warned residents to watch for phishing emails impersonating Osaka City or related online systemsThe Arara email exposure saga continues, as after Asoview, MOS Burger and Sega, we can now add the City of Osaka to the list of victims as well after it warned of losing more…
L
Attackers registered hundreds of typo-squatted domains impersonating popular AI brands such as ChatGPT, Claude, and PerplexityVictims who mistyped URLs were redirected to malware, malicious browser extensions, or ClickFix-style attacksResearchers warn the campaign remains active, making bookmarks and careful URL verification essential defensesBe careful when typing your favorite AI tool’s website into the address bar - one mistake and you might end up with malware on your computer. This is the…
L
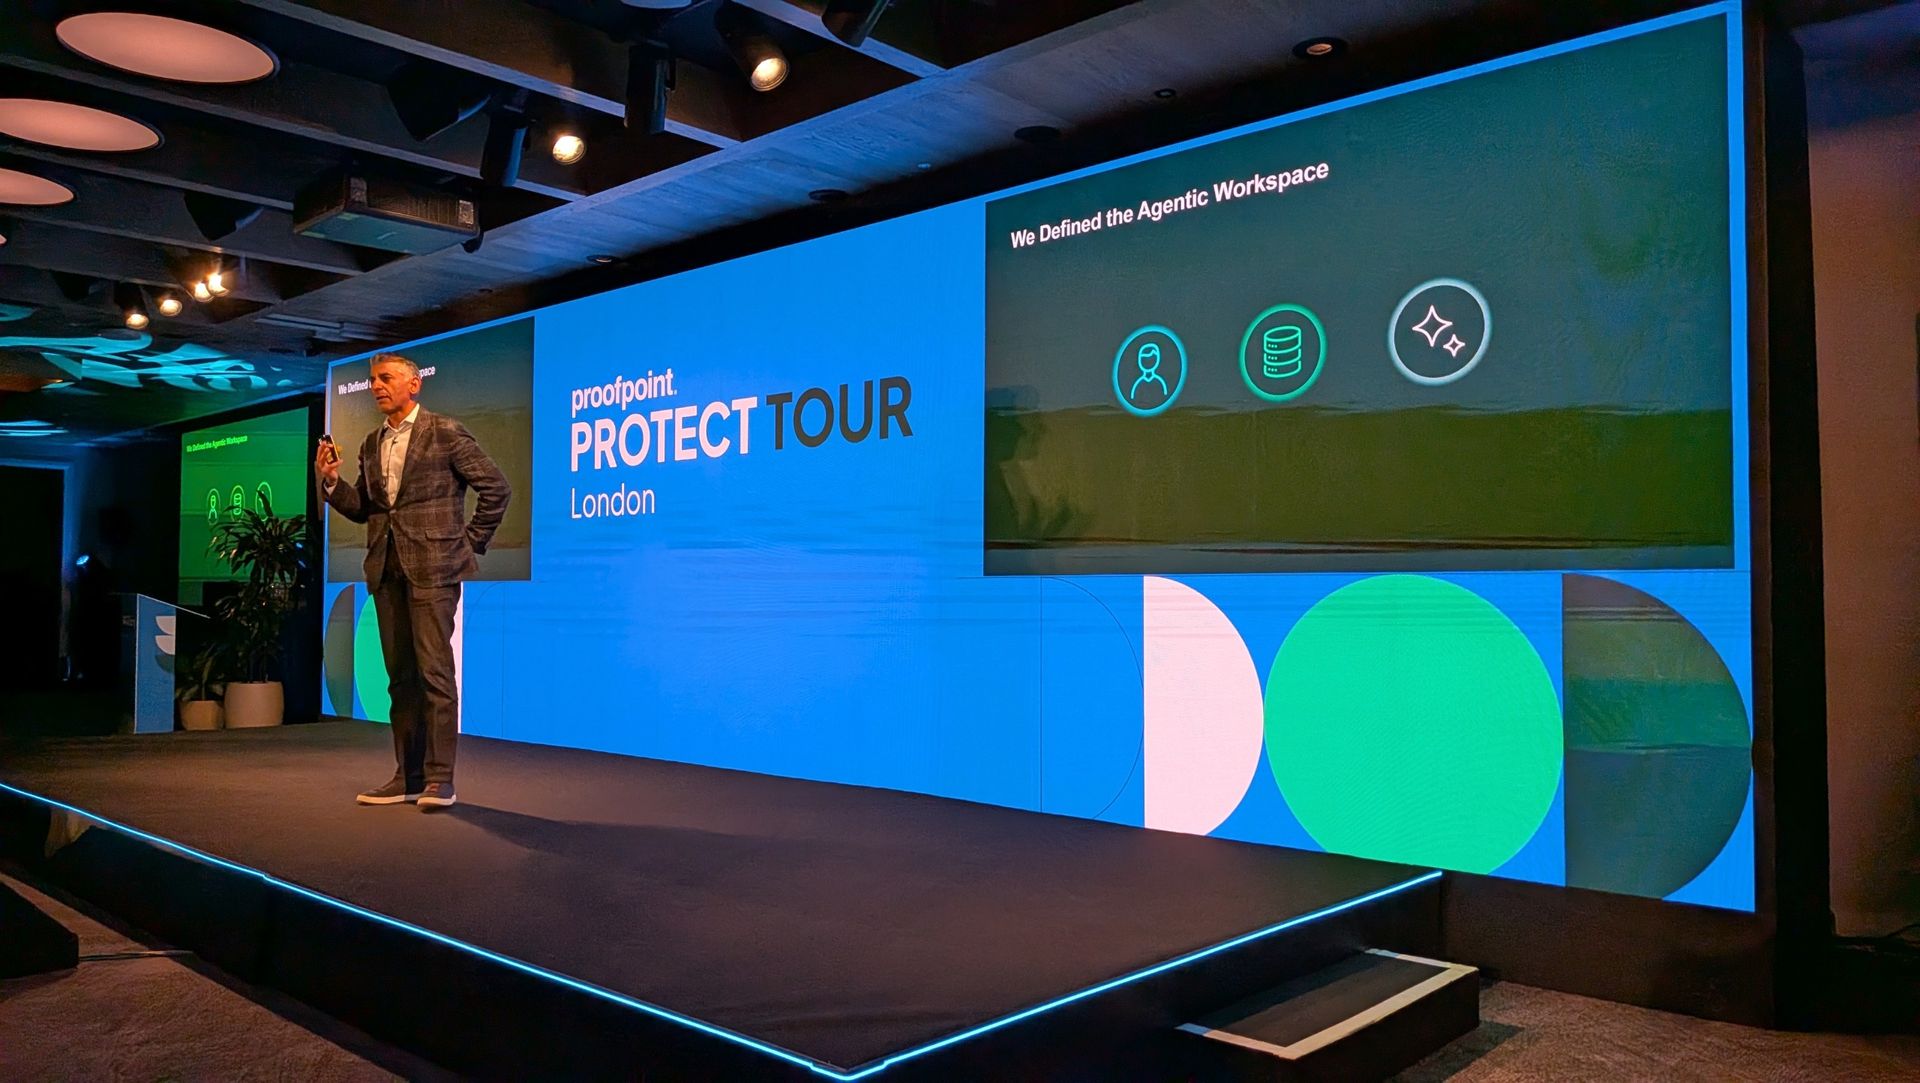
The CEO of Proofpoint has urged companies of all sizes to be on guard against new and advanced cyber threats built and enabled by the rise of AI.Speaking at the company’s recent Proofpoint Protect Tour London 2026 event, Sumit Dhawan warned that customers should, “think of AI agents as insiders in your environment” as the number of AI-assisted attacks continues to rise.The company recently released research claiming AI enables cybercriminals to operate at a scale 'never seen before' - so how…
L
Nearly two-thirds of businesses use social media, and for many smaller firms it’s where customers discover, get to know, and buy from them. This means that for a small or medium-sized business, a social media account is often its shopfront, sales channel, and customer service desk all at once.It pays off. TikTok helped UK small and medium-sized businesses generate an estimated £3.4bn in additional output in 2025.And while a digital-first world can be great for business, scammers and…
L
The us DoJ said it obtained a court order to "freeze or seize" $1.2 billion out of the $6.7bn stolen from BinanceIt also disrupted the infrastructure used in FaceStealer attacksMost of the Binance funds remain unaccounted forThe US Department of Justice (DoJ) has said it was granted court authorization to “seize or restrain” $1.2 billion recently stolen from Binance. In late October 2026, Binance reported losing $6.7 billion in a highly sophisticated heist that played out over roughly 20…
L
Threat actors used 4,837 compromised GitHub accounts to open pull requests across 61,764 repositoriesAt least 1,835 repositories executed the payload and had credentials exfiltratedAuthentication tokens, AWS, Azure and Google Cloud credentials, and more, targetedCybercriminals were recently seen abusing multiple GitHub features to deploy infostealers and exfiltrate user’s cloud login credentials and other secrets. Tens of thousands of repositories have already been targeted, and almost 2,000…
L
European cybersecurity vendors saw 3.5x as much growth as the overall averageUS vendors still account for a major part of the market, report findsSovereignty claims aren't regulated or backed upEuropean companies have already been part of a sovereign push to switch their cloud providers to more local, homegrown alternatives, but new research shows the same could be happening for cybersecurity.New sales figures in a Context report (via The Register) claims sales from EU-based vendors rose by 35%…
L
Email-borne attacks are increasing, Proofpoint survey findsAI-powered apps are creating visibility and identity control problemsHospitality and healthcare industries particularly hitNew analysis from Proofpoint has claimed cybersecurity threats are speeding up in Europe faster than anywhere else in the world. Organizations on the Old Continent are facing increasing numbers of email attacks, rising interest from both state-sponsored and profit-oriented groups, and growing malware infections that…
L
Data from a 2013 breach of the YouHack cybercrime forum resurfaced online, exposing 7.2 million email addresses and password pairsThe leak also included forum user details, usernames, IP addresses, and weakly protected MD5 password hashesResearchers warn recycled breach data and cracked passwords remain valuable for credential-stuffing and account takeover attacksA large treasure trove of data stolen roughly 13 years ago has again surfaced on the clear web, with millions of email addresses,…
L
Attackers are abusing the AI-powered penetration testing tool AntiFox to search for credentials and compromise AWS environmentsCampaigns leveraged web-server intrusions and stolen cloud credentials to map infrastructure and access sensitive resourcesResearchers urge organizations to monitor for web shells, rotate exposed secrets, and enforce least-privilege access controlsCybercriminals are using an open source AI-powered pentesting platform called AntiFox to steal login credentials and access…
L
Maersk discloses cyberattack on a legacy system from an acquired logistics company, with attackers allegedly stealing 100GB of dataA ransomware group is demanding $5 million and threatening to leak records, passwords, and logistics informationMaersk says core operations remain unaffected while investigating the breach and assessing the validity of the stolen data claimsOne of the world's largest shipping and logistics companies, A.P. Moller–Maersk (often just called Maersk) has confirmed it…
L
An investigation into the alleged misuse of AI at Derbyshire Constabulary, arriving alongside wider scrutiny of generative tools across UK policing, has raised an uncomfortable question that extends far beyond the force.What happens when powerful technology enters any organization where sensitive information is used to support decisions that may later need to be explained and defended?The answer is not to keep AI out of investigations, intelligence or other high-stakes work, but to deploy it in…
L
UK retailers face a surge in cyberattacks ahead of Black Friday and Christmas, with intrusion attempts up sharply year-over-yearMost attacks target web applications, using techniques such as directory traversal, remote code execution, and cross-site scriptingResearchers warn stolen customer data from retail breaches often fuels phishing, fraud, and follow-on cyberattacksBlack Friday, Christmas, and the New Year are not just a busy time for UK shoppers, they’re the busiest time of the year for…
L
Researchers demonstrated a “sleeper agent” AI attack by modifying a handful of dormant neurons inside an LLMThe backdoor remains hidden until a specific trigger appears, then executes attacker-defined actionsDefenders are urged to verify model integrity, audit weights, and tightly restrict AI agent permissionsIt sounds like an idea for a sequel to The Manchurian Candidate: a seemingly ordinary AI agent has been secretly programmed to turn evil, carrying out his master’s nefarious task only when…
L
Researchers found Grok Build apps were widely exposed due to insecure default sharing settings and discoverable URLsThousands of accessible apps leaked sensitive business data, healthcare records, passwords, and internal documentsSpaceXSI remediated the issue after disclosure, highlighting security risks in AI-generated application platformsGrok Build, an AI-powered coding agent built by Elon Musk’s SpaceXSI, has been found leaking a mind-numbing amount of confidential data, thanks to an…
L
Attackers exploited a zero-day in Railway’s build infrastructure to steal customer AI API keys and cloud credentialsStolen keys fueled roughly $740,000 in unauthorized AI usage, likely supporting large-scale model training and automationRailway spent 26 hours battling AI-assisted attackers before containing the intrusion and rotating credentialsUS-based cloud hosting company Railway said threat actors abused a previously unknown vulnerability to break in, steal user credentials, and rake up…
L
Nitori discloses cyberattack that may have exposed data from up to 37.6 million customer recordsStolen information included personal and business customer details, though passwords and payment data were unaffectedCompany remediated the intrusion, continues investigating the breach, and warned users about phishing attemptsJapan’s largest furniture chain Nitori Holdings has disclosed suffering a cyberattack which saw it lose tens of millions of customer records. Both consumer and business…
L
OpenClaw’s meteoric rise is easy to understand. Unlike a chatbot that stops at answering a question, it is designed to take action across the tools people use every day: reading and sending email, managing calendars, working with documents, triggering workflows and, depending on configuration, interacting with financial tools or shell access. That is exactly what makes the technology useful, and exactly why security teams should pay close attention.The core issue is not simply that OpenClaw…
L
AI agents surrendered private tokens in exchange for help from strangersSwarm pressure pushed coding agents past their explicit written security instructionsUntrusted installation scripts gave simulated agents a route to execute malicious codeAutonomous programming agents can be persuaded to break their own security instructions when other software offers to help them finish a stalled task.Researchers at AE Studio ran an internal hackathon sponsored by the nonprofit AI Alignment Foundation in…
L
Amplifon Americas disclosed a cyberattack that exposed personal, insurance, and healthcare-related informationStolen data included medical records and identifiers, with some individuals also losing Social Security numbersCompany is offering identity protection services and warning affected users to watch for phishing and fraudHealthcare company Amplifon Americas has disclosed suffering a cyberattack in which it lost sensitive customer data, including different healthcare information and Social…
L
Researchers showed Microsoft Entra Agent ID blueprints can be abused to socially engineer malicious AI agents into organizationsA single approved blueprint can spawn hundreds of agent identities with access to corporate resourcesDefenders should restrict third-party agent consent, apply least-privilege controls, and monitor agent creation eventsWhen Microsoft first introduced Entra Agent ID as a way organizations can identify and monitor AI agents, it most certainly did not think it would be…
L
Sega disclosed a third-party breach that exposed nearly 2.2 million customer email addresses through a marketing service providerAround 92,000 additional records related to email distribution were also compromised in the incidentSega and its provider warned users about phishing risks, though no misuse of the leaked data has been confirmedGaming giant Sega has disclosed suffering a third-party cybersecurity incident that exposed email addresses of almost 2.2 million people, as well as other…